TISAX Software
for your ISMS
Complaica is TISAX software for setting up, operating and evidencing an ISMS according to VDA ISA: the complete catalogue — information security, prototype protection and data protection — is assessed by maturity level per control question, measures and evidence sit on the object, the self-assessment can be retrieved at any time. Plus TISAX consulting and AI integration — from the first self-assessment to the TISAX label.
- 01VDA ISA mapped in full: information security, prototype protection, data protection
- 02Maturity level per control question, target maturity level and result with cutback — as in the ISA
- 03Self-assessment, corrective action plan and evidence for assessment levels 2 and 3
- 04AI integration (MCP) plus TISAX consulting — Co-Intelligence
- 05One system for TISAX, ISO 27001, NIS2, IT-Grundschutz and further standards
Implement and manage TISAX with Complaica
Functions with which the Complaica TISAX software covers the path from the VDA ISA self-assessment to the assessment and the TISAX label.
- 01Complete VDA ISA catalogue: information security, prototype protection and data protection as modules with all control questions
- 02Assess maturity level 0–5 per control question — with target maturity level, result per chapter and result with cutback to target maturity level, as in the ISA
- 03Assess must and should requirements and the additional requirements for high and very high protection needs separately per control question
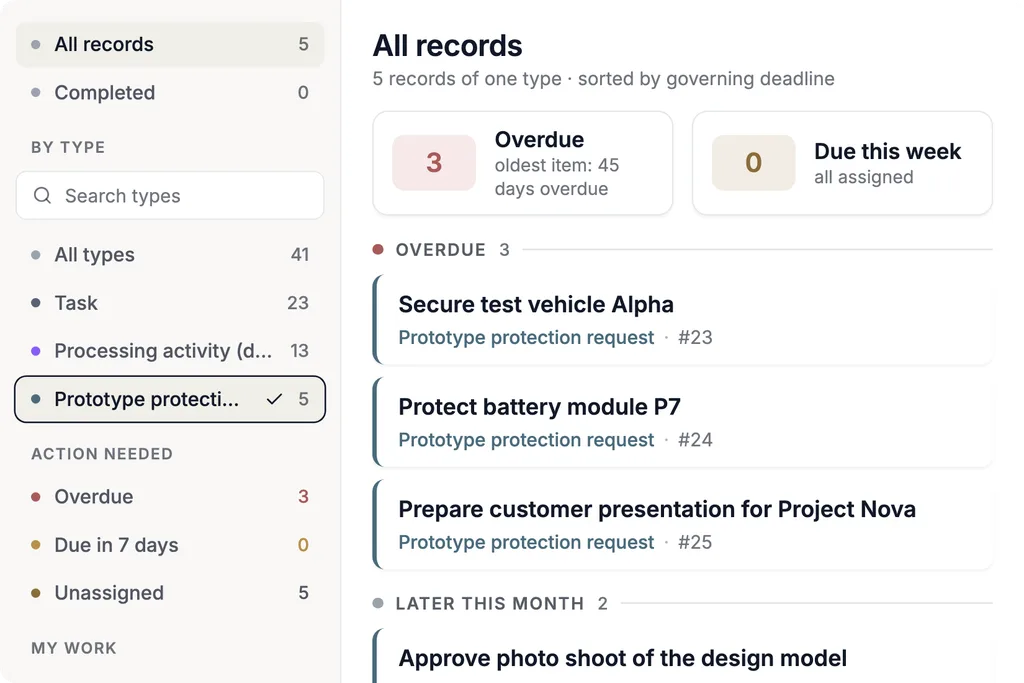
- 04Criticality and implementation status of every requirement at a glance — with owners, documents, tasks and notes
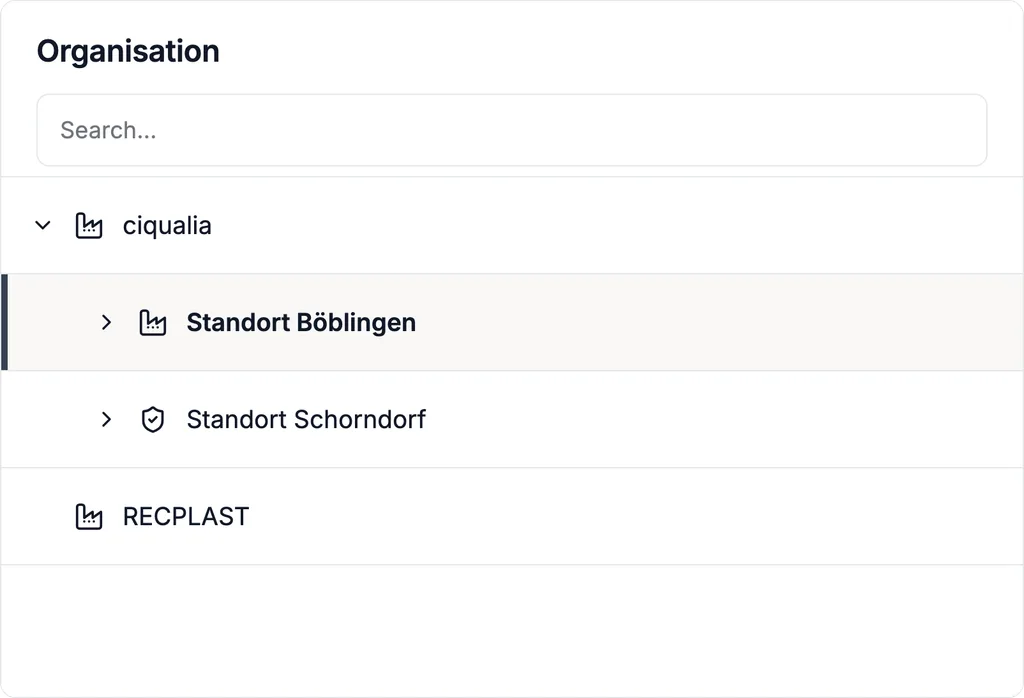
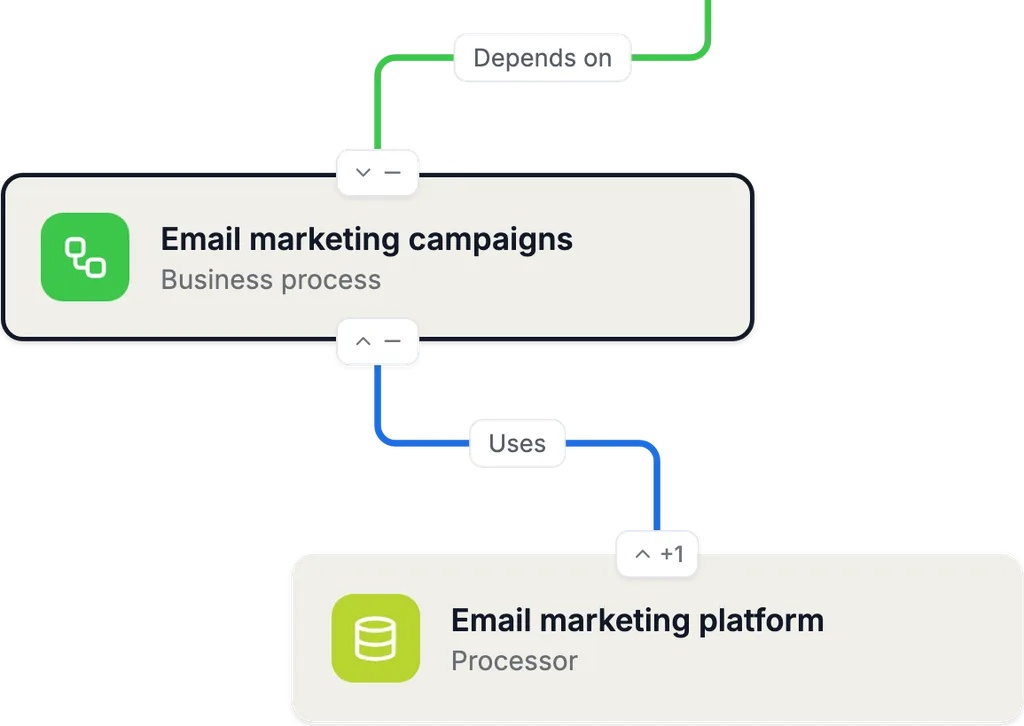
- 05Map the assessment scope per location — organisation, locations, business processes, systems and their dependencies
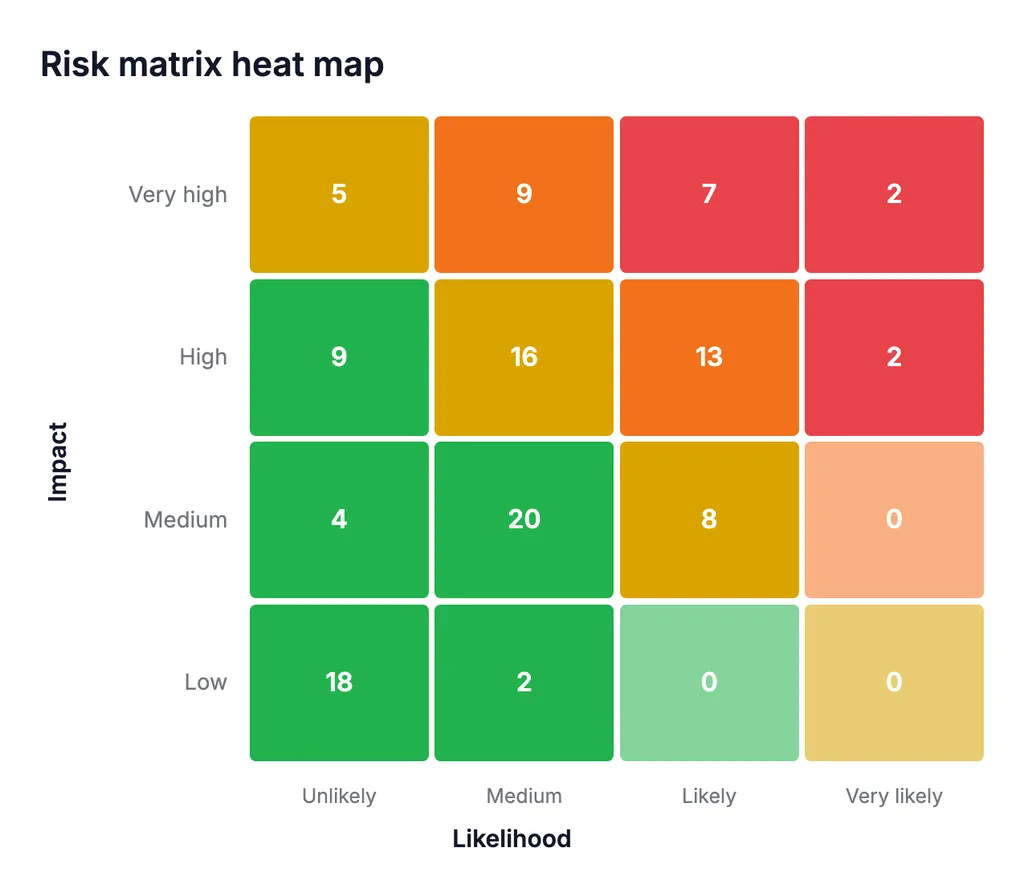
- 06Identify risks per asset and assess them in configurable risk matrices
- 07Track measures with owners, deadlines and status — as the basis for the corrective action plan and the follow-up assessment
- 08Store evidence on the object it belongs to — documents, links and assessments with author and date, the way the audit provider wants to see them
- 09PDCA cycle: self-assessment, measures, effectiveness review and improvement in one data set — after the label too
- 10Reports and dashboards for management and assessment preparation — Excel-like maturity level views
- 11Integration with Microsoft Azure, SAP, Jira and further systems; import and export from and to Excel
- 12AI integration (MCP) for questions on VDA ISA, control questions and maturity levels, and on using the tool
TISAX VDA ISA dashboards: Excel-like, but connected
The VDA ISA is an Excel file. Complaica shows the maturity levels the same way — only on a connected data set instead of in cells.
The green line marks the target maturity level per chapter. To prepare for the TISAX assessment, your maturity levels — the blue bars — should sit on or above this line.
The result with cutback to target maturity level shows progress: values above the target are cut back to 3 — the way the ISA itself calculates — so a chapter at level 5 does not make up for another at level 1. A value near 3.0 is an indication, not proof of readiness: ready is whoever fulfils every applicable requirement and can prove it with evidence.
For the TISAX label you fill in the self-assessment on the basis of the ISA: for every control question in the information security, prototype protection and data protection catalogues you determine which maturity level your ISMS reaches. Complaica assesses the maturity level per control question and rolls it up to sub-chapters, chapters and the overall result.
From the VDA ISA in Excel to a central ISMS
The self-assessment can be kept in the ISA file — until responsible persons, deadlines, evidence and a second standard come in. Four points where Complaica organises the work differently.
| VDA ISA in Excel | Complaica | |
|---|---|---|
| Taking over existing assessments | The assessments live in the file; a new ISA version means transferring them again. | Import from and export to Excel; our specialists accompany the transfer of existing data. With a new catalogue version, assessments and evidence are kept. |
| Responsible persons, deadlines and measures | Names and dates in columns, kept current by hand. | Measures with responsible persons, deadlines and status; every status change is recorded with author and date — the basis for the corrective action plan and the follow-up. |
| Assigning evidence to requirements | References to files in shared folders. | Documents, links and assessments sit on the object and are assigned to the control question — the way the audit provider wants to see them. |
| Shared data for several standards | One file per standard, duplicate maintenance between them. | The same assets, risks, measures and evidence for TISAX, ISO 27001, NIS2 or IT-Grundschutz — where the content fits. |
Complaica ISMS modules for TISAX
Seven modules, one connected data set: organisation, assets, ISA catalogue, risks, reports, tasks and integrations work on the same objects.
01 / 07 · Organisation management
Organisation, locations and assessment scope
TISAX is assessed per location. Map your organisation as a tree — entities, locations, departments, units — and define which locations and units belong to the assessment scope. Responsibilities are assigned per unit and per object; access rights follow the same structure.
02 / 07 · Asset structure analysis
Assets, dependencies and business processes
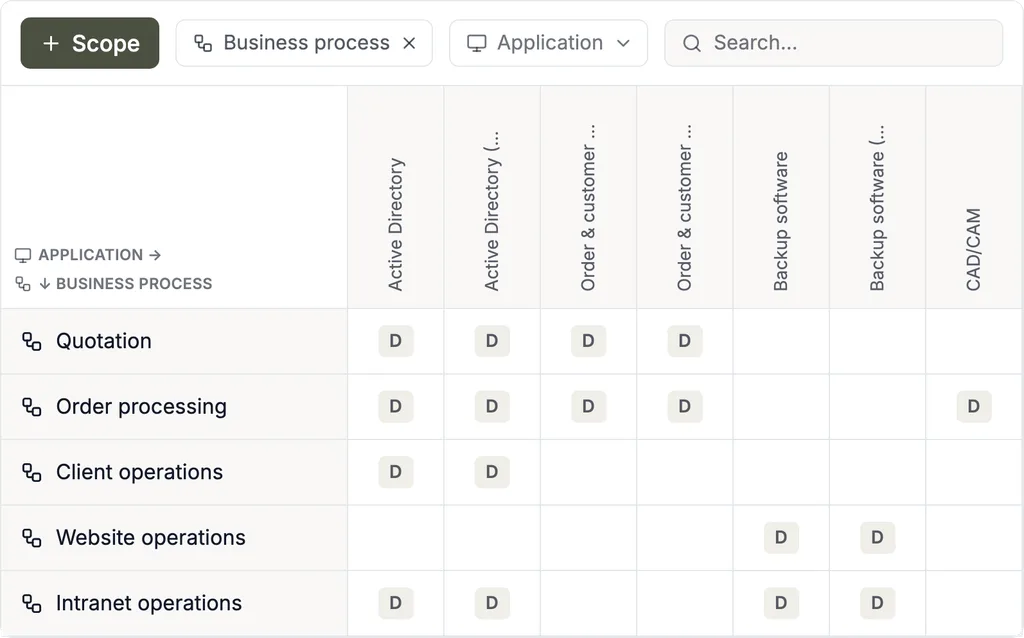
Record assets — applications, systems, data, locations, service providers — with type and further attributes, and link them to the business processes that depend on them. Assets can be imported from asset management, CMDBs, Microsoft Azure and other sources.
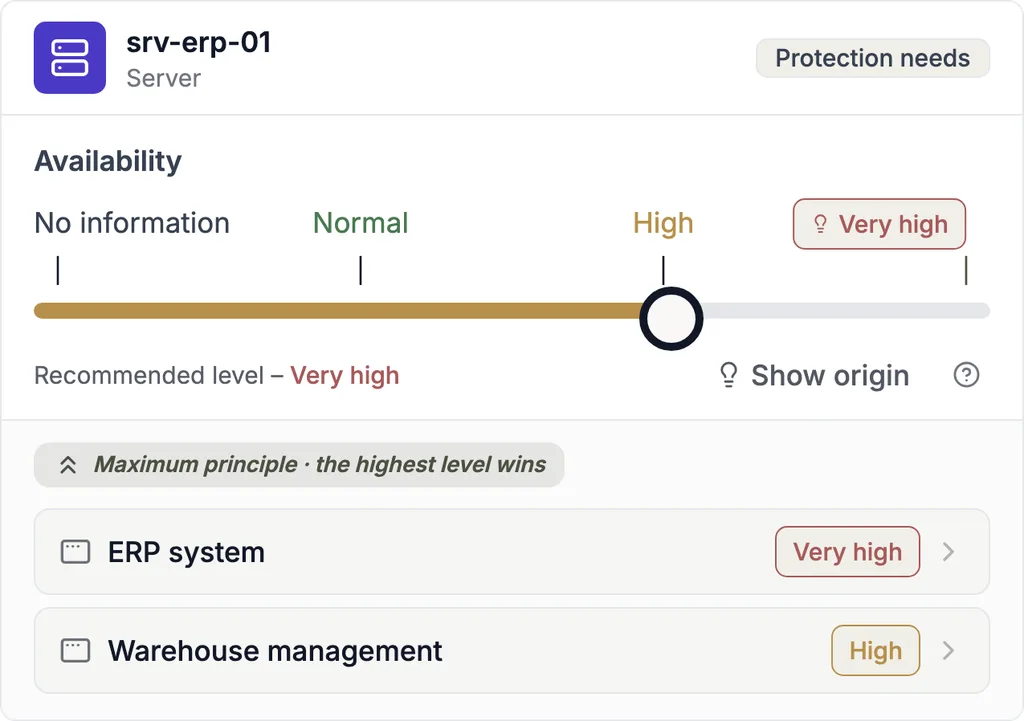
Dependency graphs and matrices are the basis for protection needs and risk analysis: the protection need — normal, high, very high — is inherited along the dependencies, a risk is assigned to the asset it concerns.
03 / 07 · Compliance management
VDA ISA catalogue, maturity levels and target maturity level
Assess every control question of the VDA ISA — information security, prototype protection and data protection — with a maturity level from 0 to 5 on your asset tree. Must and should requirements and the additional requirements for high and very high protection needs are assessed separately; the maturity level cumulates to sub-chapter, chapter and the overall result with cutback to target maturity level.
Your own requirement catalogues and further standards are assessed on the same model — the same assets, the same evidence. What is documented for ISO 27001 can — where it fits in substance — be used for the ISA.
04 / 07 · Risk management
Risk analysis, risk assessment and risk treatment
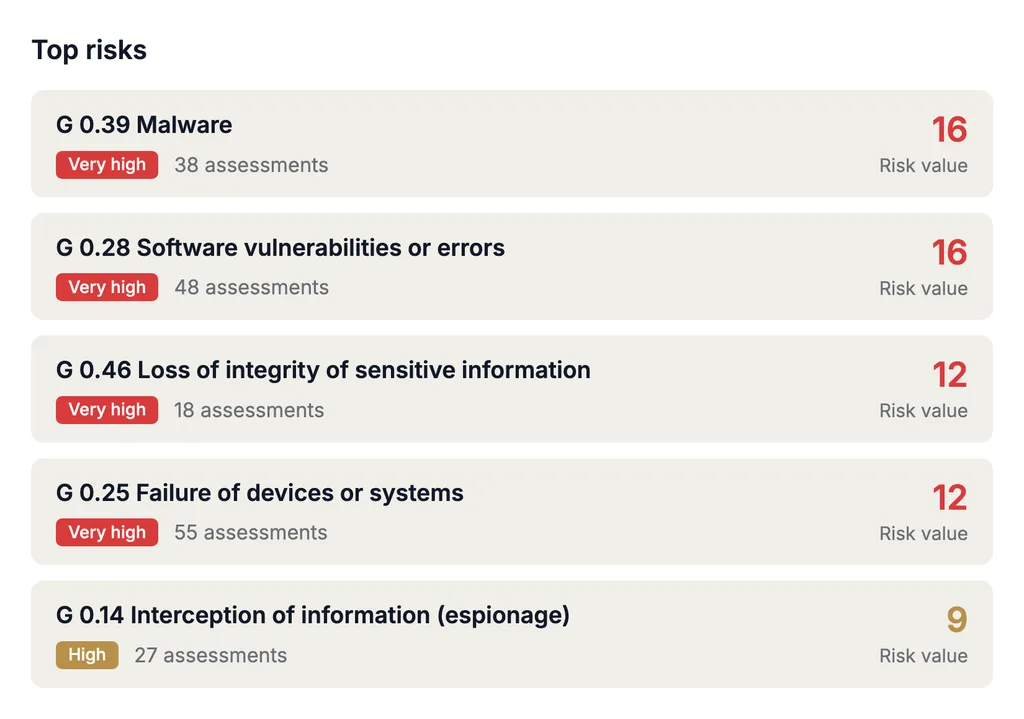
The ISA requires information security risk management: identify threats per asset — from standard or your own threat catalogues — and assess likelihood and impact in a configurable risk matrix. For every risk the treatment option is set, linked to control questions and measures, and the residual risk is tracked over time.
05 / 07 · Reporting & data analysis
Reports for management, self-assessment and corrective action plan
Generate maturity level reports per chapter and control question, the corrective action plan for deviations and risk reports from your own data — as a report template or as a custom report. Dashboards show management the state before the assessment; distribution is handled by the Complaica Teams integration and the mail bot, and external BI and data analysis tools read the data over the REST API or data marts.
06 / 07 · Task management & collaboration
Measures, owners and deadlines
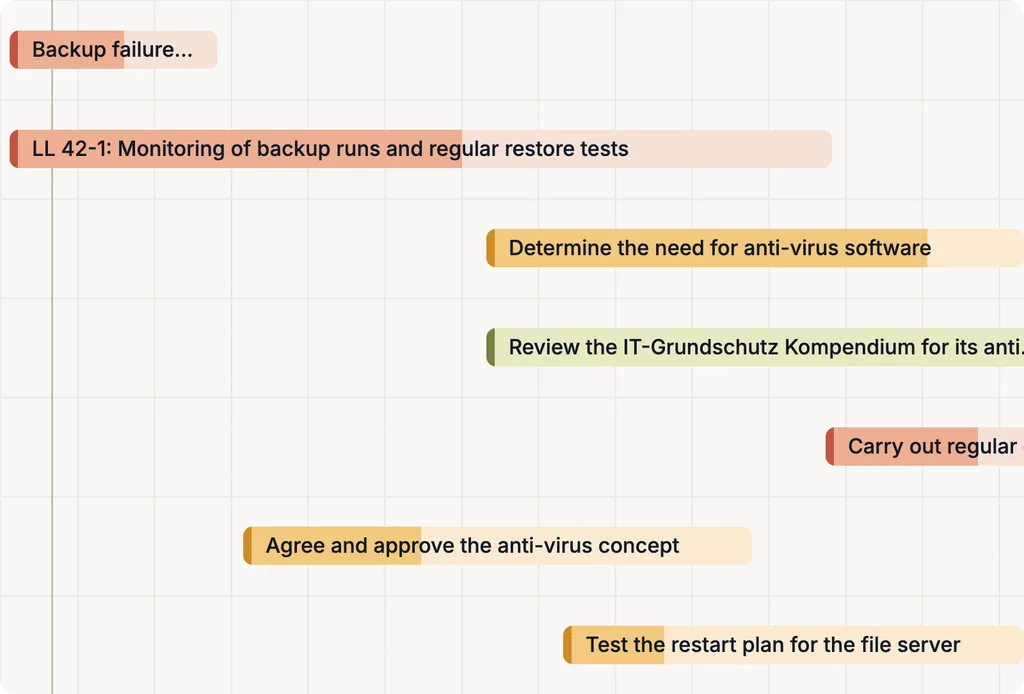
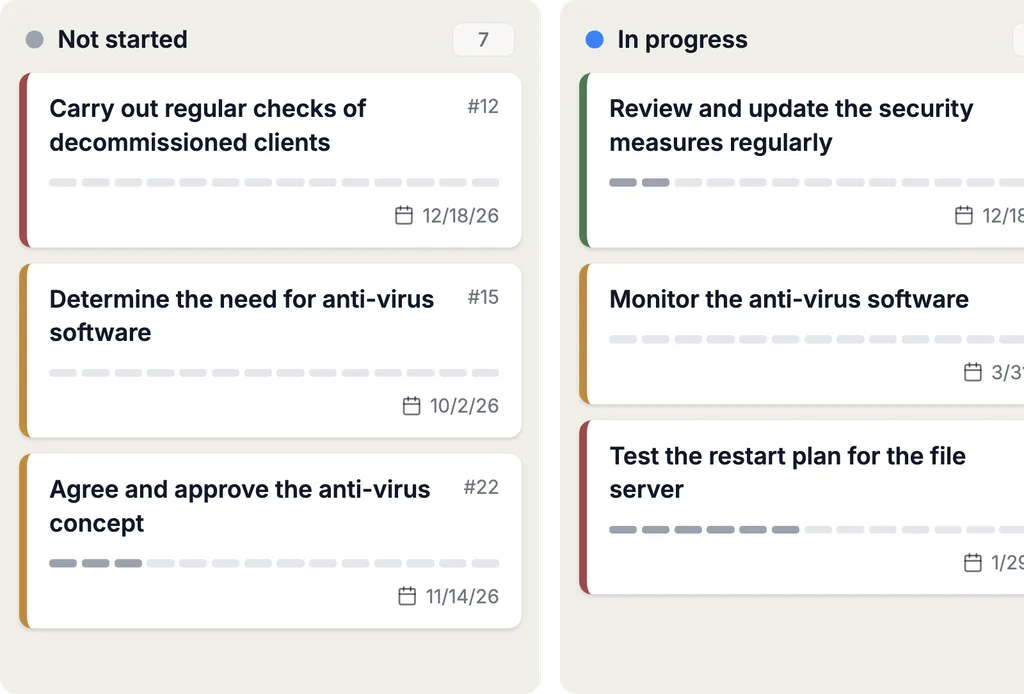
Measures and tasks carry owners, deadlines and status; every status change is recorded with author and date. Internal and external parties — the audit provider or service providers in scope, say — work in the same system: access to individual assets and documents is granted per object and by link.
07 / 07 · Integrations & automation
Complaica integrations
Over the REST API Complaica connects asset management and CMDB systems — Microsoft Azure, i-doit, GLPI, FNT Command and others — and keeps the asset inventory in the ISMS in step with reality. Jira, Microsoft Planner and others can be connected as task systems.
Application data is available through preset data marts, the REST API or MCP for external analysis and reporting systems.
How the TISAX assessment works
TISAX (Trusted Information Security Assessment Exchange) is the automotive industry’s assessment and exchange mechanism for information security, operated by the ENX Association. Its basis is the VDA ISA (Information Security Assessment), which takes up essential requirements of ISO/IEC 27001 and adds industry-specific criteria — prototype protection, for instance.
The results are shared over the ENX TISAX platform: a participant chooses an accredited audit provider, is assessed once and releases the result to the partners who are meant to see it. All participants recognise the standardised result — one assessment instead of several audits by different customers.
Assessment levels, protection needs and assessment objectives
Assessment Level 1
Normal protection need · Self-assessment
Not used in TISAX, but useful as a self-assessment for internal purposes. An auditor only establishes that a completed self-assessment exists; its content is not checked. A partner may also request a self-assessment outside TISAX.
Assessment Level 2
High protection need · Plausibility check
The audit provider checks your self-assessment for plausibility, inspects evidence and interviews the responsible persons — usually by web conference, with an on-site visit on request.
Assessment objectives include: Confidential, High availability, Test vehicles, Proto events, Data
Assessment Level 3
Very high protection need · On-site assessment
The audit provider verifies the implementation comprehensively: documents and evidence, planned interviews with process owners, inspection of the locations, observation of the processes and unplanned interviews with staff. On-site presence is mandatory.
Assessment objectives include: Strictly confidential, Very high availability, Proto parts, Proto vehicles, Special data
ISA 2027: what changes
ENX has published VDA ISA 2027. What decides the catalogue version is the date the assessment is ordered — not the registration of the scope and not the kick-off.
- Assessments ordered from 2027
Assessments ordered in 2027 are conducted against ISA 2027. Assessments ordered before 1 January 2027 can still be carried out under ISA 6.
- Last date for ISA 6
According to ENX, an initial assessment under ISA 6 can be opened for the last time in March 2027. ENX provides a redline version comparing ISA 6.0 and ISA 2027.
- The catalogue in Complaica
Complaica updates its catalogues with new versions of a standard; existing assessments and evidence are kept. We will tell you the state of the ISA 2027 implementation on request.
ENX information as of 7 October 2026
Five steps to the TISAX label
From the first look into the ISA to the shared result — and what Complaica takes over in each step.
- 01
Get to know
Get to know the VDA ISA and its control questions: which assessment objectives your customers require, which protection need applies, which locations belong to the scope. In Complaica the catalogue is ready, with explanations.
- 02
Prepare
Register as a participant in the ENX portal, define assessment objectives and scope, choose an audit provider. The self-assessment according to the ISA in Complaica shows maturity levels and gaps before the auditor sees them.
- 03
Be assessedAssessment Level 2 or 3
Depending on the assessment objective, the audit provider assesses by web conference (AL 2) or on site (AL 3): document review, interviews, clarification of possible deviations. Evidence and reports come from Complaica.
- 04
Share the result
The audit provider posts the TISAX report on the ENX platform; you decide which participants see the result. The label is valid for three years.
- 05
ImproveCorrective action plan and follow-up
For deviations, a corrective action plan is submitted to the audit provider and checked in the follow-up assessment — only then is the report complete. Measures, deadlines and evidence for it keep running in Complaica.
Why implement TISAX?
What a TISAX label brings suppliers and service providers of the automotive industry.
- 01Credibility as a trusted partner for OEMs and suppliers — the label is the industry’s common language
- 02One assessment instead of many: the shared result replaces repeated information security audits by individual customers — and saves time and budget
- 03Reduce risks through effective risk management, as the ISA requires
- 04New business: many OEMs require the label as a precondition for working together
- 05A uniform standard for information security, aligned with the requirements of the automotive industry — prototype protection included
- 06Measure the maturity level of your own information security controls and make it comparable
- 07Greater information security awareness among staff
Why Complaica as TISAX software?
Six reasons automotive suppliers prepare their TISAX assessment with Complaica.
TISAX consulting from one source
Our TISAX consultants accompany the whole implementation — from gap analysis through the self-assessment to the follow-up assessment — and guide you through every function of the product.
One solution for several standards
ISO 27001, NIS2, IT-Grundschutz or data protection management are run in the same system: shared assets, risks and evidence, visible dependencies and one status for everything.
Granular view of the TISAX requirements
Every control question is assessed individually — must, should and additional requirements for high and very high protection needs separately. That makes the assessment more transparent and the decision on the maturity level easier.
PDCA cycle included
The tool supports Plan-Do-Check-Act: it helps not only up to the label but improves the ISMS continually — and so prepares the renewal after three years.
Complete VDA ISA catalogue
The control questions of the information security, data protection and prototype protection catalogues are included as modules; every requirement is assessed with a maturity level. When a new ISA version appears, the catalogue is updated.
Criticality and implementation status at a glance
Implemented requirements are marked and show owners, documents, tasks and notes. Requirements are fulfilled through tasks or individual controls — or assessed by self-assessment.
Streamline compliance tasks with AI assistance
With the optional AI integration (MCP), Complaica answers questions on the VDA ISA, explains control questions and maturity levels, helps with measures and tasks and finds answers in your own policies and documents. It supports the work towards the assessment — evaluation and decision stay with you.
- 01Answer questions on TISAX and VDA ISA
- 02Explain control questions and maturity levels — what is required and what counts as evidence
- 03Suggest, formulate and assign measures and tasks
- 04Analyse your policies, procedures and documents and answer questions about them
- 05Explain how to use Complaica — which function for what
Customer voices on the ISMS with Complaica
“We can do everything we need in one tool”
Complaica is extremely user-friendly and customising it is child’s play. We can take care of ISO compliance and data protection with it — we can do everything we need in one tool. For us, Complaica is better than the alternatives on the market and cheaper at the same time.
More …Less
Complaica is extremely user-friendly and customising it is child’s play. We can take care of ISO compliance and data protection with it — we can do everything we need in one tool.
For us, Complaica is better than the alternatives on the market and cheaper at the same time.
“The optimised compliance process”
One of the features we like best about Complaica is the optimised compliance process. The user interface has a clear, structured design that offers more usability and encourages a higher working speed. This not only gives new users a steep learning curve, it also lets experienced users minimise their effort. In every phase of the security management lifecycle, recurring tasks such as scoping, structure analysis, modelling and even the tracking of risks and measures are supported by a wealth of functionality. On top of that the platform’s performance is great — it is stable and excellent in terms of speed.
More …Less
One of the features we like best about Complaica is the optimised compliance process. The user interface has a clear, structured design that offers more usability and encourages a higher working speed. This not only gives new users a steep learning curve, it also lets experienced users minimise their effort.
In every phase of the security management lifecycle, recurring tasks such as scoping, structure analysis, modelling and even the tracking of risks and measures are supported by a wealth of functionality.
On top of that the platform’s performance is great — it is stable and excellent in terms of speed.
“The guided approach played a decisive role for us”
We were new to compliance and to implementing ISO 27001, and had to go through the complicated certification process. Given the regulatory complexity, we wanted to find the best way for us to get started. Our project manager (aka security officer) had never worked with such compliance standards and rules before. So we decided on support from a third party — Complaica, to be precise. The guided approach played a decisive role for us. Complaica had all the detailed explanations for the compliance check and the risk analysis, including practical suggestions.
More …Less
We were new to compliance and to implementing ISO 27001, and had to go through the complicated certification process.
Given the regulatory complexity, we wanted to find the best way for us to get started. Our project manager (aka security officer) had never worked with such compliance standards and rules before.
So we decided on support from a third party — Complaica, to be precise. The guided approach played a decisive role for us. Complaica had all the detailed explanations for the compliance check and the risk analysis, including practical suggestions.
TISAX consulting
Consulting along the TISAX process — from gap analysis to follow-up assessment, to the extent you need.
- Gap analysis and readiness check
Comparison of your current state with the control questions of the VDA ISA for your assessment objectives. Result: maturity levels per chapter, a prioritised list of gaps and an implementation plan.
- Setup and introduction of the ISMS
Scope per location, organisation, asset structure and roles are set up in Complaica. You get a working ISMS that covers the requirements of the ISA.
- Self-assessment and evidence
Support with the self-assessment according to the ISA — justifying maturity levels, assigning evidence, closing gaps — until the result with cutback to target maturity level holds.
- Prototype protection and data protection
The additional catalogues for prototype parts, vehicles and events and for personal data under Art. 28 GDPR — implemented organisationally and physically.
- Preparation for assessment and follow-up
Prepare interviews and the on-site inspection, provide documents and evidence the way the audit provider wants to see them, set up the corrective action plan for deviations.
- External information security officer
A contact for your ISMS, for a time or permanently — for organisations without a role of their own for it.
SaaS or on-premises
Complaica runs where your organisation needs it — the licence costs the same either way.
- SaaS, hosted in Germany
The SaaS variant is operated in Germany; you work in the browser, without infrastructure of your own.
- On-premises in your infrastructure
You run Complaica in your own environment — for organisations whose data may not leave the house.
- Taking over existing data
Import and export from and to Excel and over the REST API; our specialists accompany the transfer of your data free of charge.
Manage TISAX and ISO 27001 together
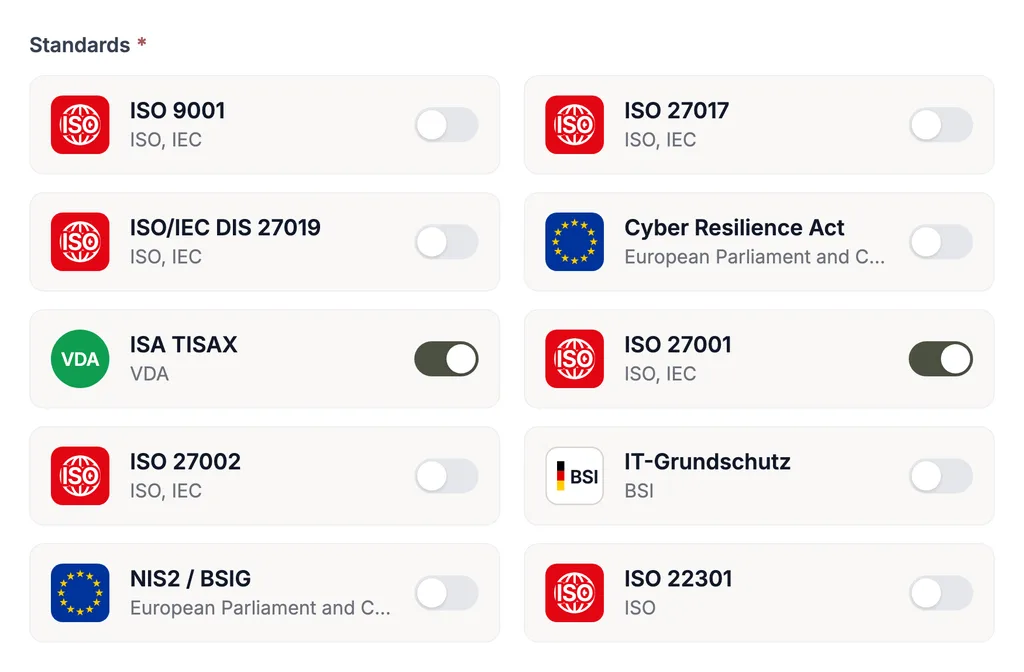
TISAX is rarely the only standard that applies to a supplier. In Complaica the requirements of further standards use the same assets, risks, measures and evidence: what is documented for the VDA ISA can — where it fits in substance — be used for an ISMS according to ISO 27001, for NIS2, IT-Grundschutz or data protection management under the GDPR. No duplicate maintenance.
Every standard ships with its requirement catalogue; your own catalogues can be added at any time.
Frequently asked questions about TISAX software
What is TISAX?
TISAX (Trusted Information Security Assessment Exchange) is the assessment and exchange mechanism for information security in the automotive industry — developed by the German Association of the Automotive Industry (VDA) and operated by the ENX Association. A participant is assessed once by an accredited audit provider according to the VDA ISA and shares the result over the ENX platform with the partners of its choice. TISAX is a registered trade mark of the ENX Association.
What is the VDA ISA?
The VDA ISA (Information Security Assessment) is the requirement catalogue TISAX assessments are carried out against. It consists of the catalogues information security (chapters 1–7: policies and organisation, human resources, physical security, identity and access management, IT security/cyber security, supplier relationships, compliance), prototype protection (chapter 8) and data protection (chapter 9). Every control question is assessed with a maturity level from 0 to 5; the target maturity level is usually 3. ISA 6 is currently in force; assessments ordered from 2027 run according to ISA 2027.
What is TISAX software?
TISAX software maps the VDA ISA as a catalogue and links it to the components of your ISMS — scope, locations, assets, risks, measures and evidence. Instead of maintaining the ISA Excel file by hand, you assess every control question once on the object, and maturity levels per chapter, the result with cutback to target maturity level and the corrective action plan arise from the data.
Which assessment levels are there in TISAX?
Three. Assessment Level 1 is a self-assessment without a check of its content and is not used in TISAX. At Assessment Level 2 (high protection need) the audit provider checks the self-assessment for plausibility, inspects evidence and conducts an interview — usually by web conference. At Assessment Level 3 (very high protection need) the audit provider assesses on site: documents, planned and unplanned interviews, inspection of the locations and observation of the processes.
What are TISAX assessment objectives?
Assessment objectives define what is assessed and at which assessment level. They cover information security (confidentiality and availability, each at two levels), prototype protection (prototype parts and components, prototype vehicles, test vehicles, events and shootings) and data protection (under Art. 28 GDPR, with or without special categories of personal data). Which assessment objectives you need is usually specified by your customers.
Is TISAX a certification?
Formally not: TISAX does not issue a certificate but a TISAX label per assessment objective, which the audit provider posts on the ENX platform after a passed assessment. In practice people nevertheless often speak of “TISAX certification”. The label is valid for three years; after that a new assessment is needed.
How does a TISAX assessment work?
Registration as a participant in the ENX portal with assessment objectives and scope (locations); choice of an audit provider; self-assessment according to the ISA; assessment at level 2 or 3; for deviations, a corrective action plan and a follow-up assessment; report on the ENX platform, which you release to partners. With Complaica, self-assessment, evidence and corrective action plan come from one data set.
How does Complaica support the TISAX self-assessment?
The VDA ISA is included in full as a catalogue. You assess every control question with a maturity level on your asset tree — must, should and additional requirements separately — and store evidence and measures on the object. Dashboards show maturity levels per chapter against the target maturity level and the result with cutback, the way the ISA calculates.
What do target maturity level and “result with cutback” mean?
The ISA sets a target maturity level for every control question, usually 3. For the “result with cutback to target maturity level”, maturity levels above the target are cut back to the target before the average is taken: a chapter at maturity level 5 does not make up for another at maturity level 1. The value shows progress — ready for the assessment is whoever fulfils every applicable requirement and can prove it with evidence, not whoever reaches a number.
How does TISAX relate to ISO 27001?
The VDA ISA takes up essential requirements of ISO/IEC 27001 and adds industry-specific ones — prototype protection, data protection, supplier relationships in the automotive chain. An ISMS according to ISO 27001 is a good foundation but does not replace the TISAX assessment; conversely, ISO 27001 documentation can — where it fits in substance — be used for the ISA. In Complaica both are run on the same data set.
Does Complaica support prototype protection and data protection according to the ISA?
Yes. The catalogues prototype protection — physical and organisational requirements, handling of vehicles, components and parts, test vehicles, events and shootings — and data protection are included as modules of their own and, like information security, are assessed per control question with a maturity level.
Can an existing self-assessment be taken over from Excel?
Yes. Complaica imports and exports data from and to Excel and over the REST API; migrating your data is free and accompanied by our specialists. So you evaluate the tool on your own data set rather than on demo data.
Can Complaica manage several standards at once?
Yes. ISO 27001, NIS2, IT-Grundschutz, GDPR, ISO 22301 and further standards are assessed on the same model and use the same assets, risks, measures and evidence. What is documented for TISAX can be used for the other standards where it fits in substance.
How long does it take to obtain the TISAX label?
Typically three to twelve months from start to label — depending on assessment objectives, number of locations, existing ISMS and resources; waiting times for registration and the assessment date come on top. If deviations remain, corrective action plan and follow-up assessment follow within the period ENX sets for them. The label is valid for three years.
How much does TISAX cost?
Three parts: the ENX participation fee for registration and platform, the assessment by the audit provider — depending on assessment level, assessment objectives and number of locations — and the effort for setting up and running the ISMS (internal time, consulting, software). Complaica lowers the third part: the prepared catalogue, the evidence generated from the data and the AI integration save most of the documentation work. Complaica lowers the third part: the prepared catalogue, the evidence assigned on the object and the AI integration reduce the manual documentation work.
Who is TISAX relevant for?
For suppliers, development and engineering service providers, IT service providers, agencies and everyone who handles confidential information, prototypes or personal data of manufacturers and tier-1 suppliers. As a rule the customer requires the label with specific assessment objectives as a precondition for working together.
What changes with ISA 2027?
ENX has published the VDA ISA 2027; it becomes the basis of TISAX assessments ordered from 2027. Initial assessments according to ISA 6 can still be opened until March 2027. In Complaica the catalogue is updated with the new version; existing assessments and evidence migrate with it.
Sources References and legal sources
5 sources · TISAX, VDA ISA, TISAX-Teilnehmerhandbuch, ISO/IEC 27001, … Show Hide
Norms & standards
Guidelines & official publications
-
TISAX-Teilnehmerhandbuch TISAX Participant Handbook (opens in a new tab)
Only the version published in the respective official journal is legally binding. Standards are available from the publishers named.
Start TISAX with Complaica
Test Complaica, request a demo or talk about your existing self-assessment and a migration — write to us.
Thank you.
We will get back to you within one business day.
Not sent.
That did not work. Please check the fields or email us directly.