ISMS Software
for ISO 27001
Complaica supports the introduction, operation and continual improvement of an information security management system (ISMS) according to ISO/IEC 27001:2022. Assets, risks, controls/measures and evidence are maintained centrally and audits are prepared systematically — with AI integration.
- 01ISO 27001 from scope to audit — in one data set
- 02Guided setup and operation of the ISMS
- 03Risks, controls and evidence managed centrally
- 04AI integration (MCP) plus expert consulting — Co-Intelligence
- 05Ready-to-use content for ISO/IEC 27001 (ISMS), Annex A / ISO/IEC 27002 (controls) and ISO/IEC 27005 (risk management)
Implement and manage ISO 27001 with Complaica
Functions with which the Complaica ISMS software covers the path from the requirements of ISO/IEC 27001:2022 to the audit evidence.
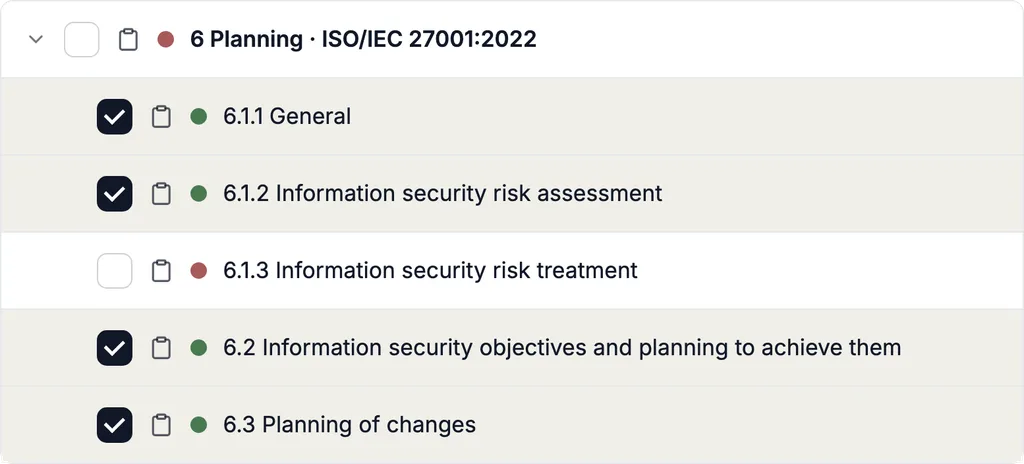
- 01Assess the requirements of ISO/IEC 27001:2022 — implementation level per requirement, cumulated up to the top level
- 02Select and assess the 93 Annex A controls of ISO/IEC 27001:2022 and link them to requirements, assets and risks — with implementation guidance from ISO/IEC 27002:2022
- 03Map the ISMS scope and asset structure — organisation, business processes, systems and their dependencies
- 04Identify risks per asset and assess them in configurable risk matrices
- 05Plan risk treatment — treatment option, measures and residual risk documented traceably
- 06Track measures with owners, deadlines and status
- 07Store evidence on the object it belongs to — documents, links and assessments with author and date
- 08Create the Statement of Applicability (SoA) on the basis of requirements, risk treatment and controls, and keep it current
- 09Reports and dashboards for management review and audit preparation
- 10Integration with Microsoft Azure, SAP, Jira and further systems; outlook, table, matrix and graph views, import and export from and to Excel
- 11AI integration (MCP) for questions on ISO 27001, requirements and controls, and on using the tool
Complaica ISMS modules for ISO 27001
Modules, one connected data set: organisation, assets, requirements, risks, reports, tasks and integrations work on the same objects.
01 / 07 · Organisation management
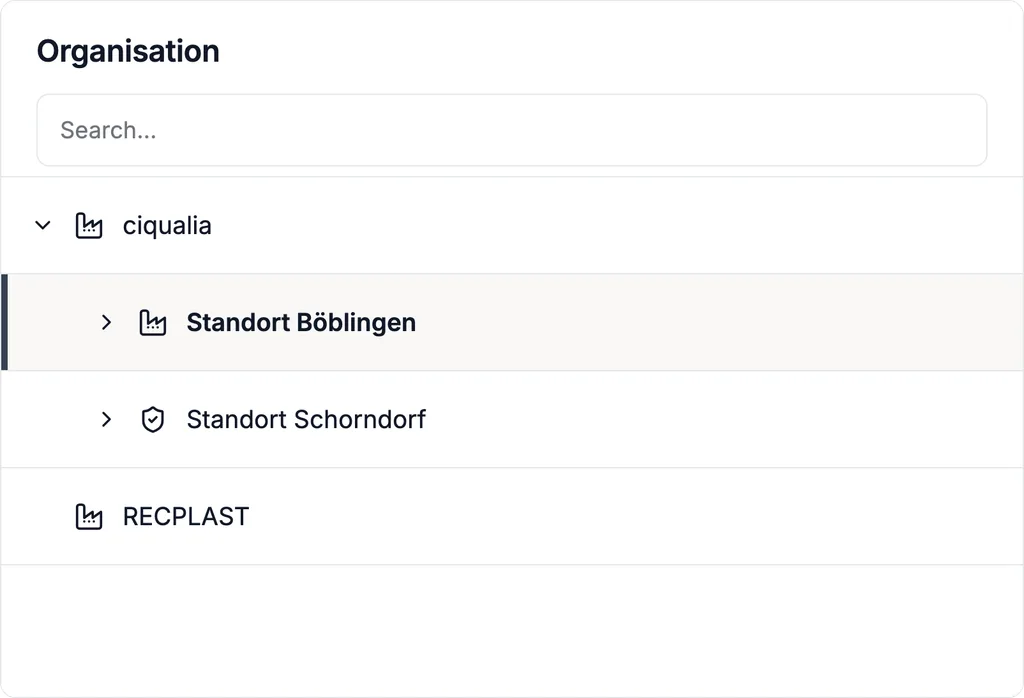
Organisation, sites and ISMS scope
Map your organisation as a tree — entities, sites, departments, units — and define which parts belong to the scope of the ISMS. Responsibilities are assigned per unit and per object; access rights follow the same structure.
02 / 07 · Asset structure analysis
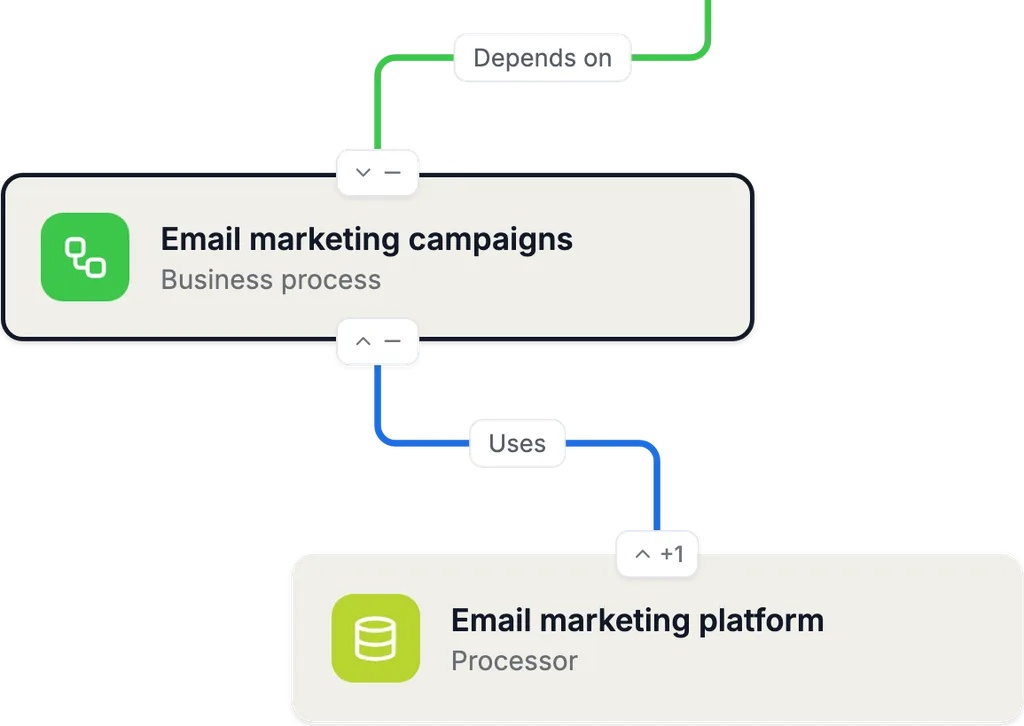
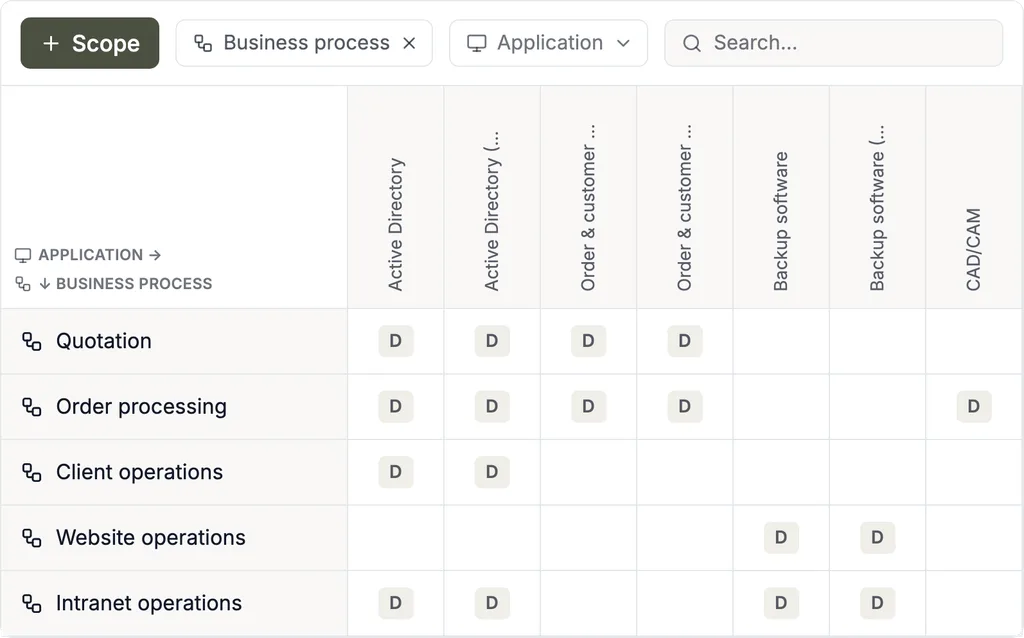
Assets, dependencies and business processes
Record assets — applications, systems, data, sites, service providers — with type and further attributes, and link them to the business processes that depend on them. Assets can be imported from asset management, CMDBs, Microsoft Azure and other sources.
Dependency graphs and matrices are the basis for protection needs and risk analysis: protection needs are inherited along the dependencies, a risk is assigned to the asset it concerns.
03 / 07 · Compliance management
Requirements, Annex A controls, implementation status, SoA
Assess the requirements of ISO/IEC 27001:2022 and the 93 Annex A controls of the standard — with implementation guidance from ISO/IEC 27002:2022 — on your asset tree. Every control receives an implementation status, a justification and evidence; the status cumulates bottom-up to the organisation.
The Statement of Applicability (SoA) is built on the basis of the requirements and controls. Your own requirement catalogues and further standards are assessed on the same model — the same assets, the same evidence.
04 / 07 · Risk management
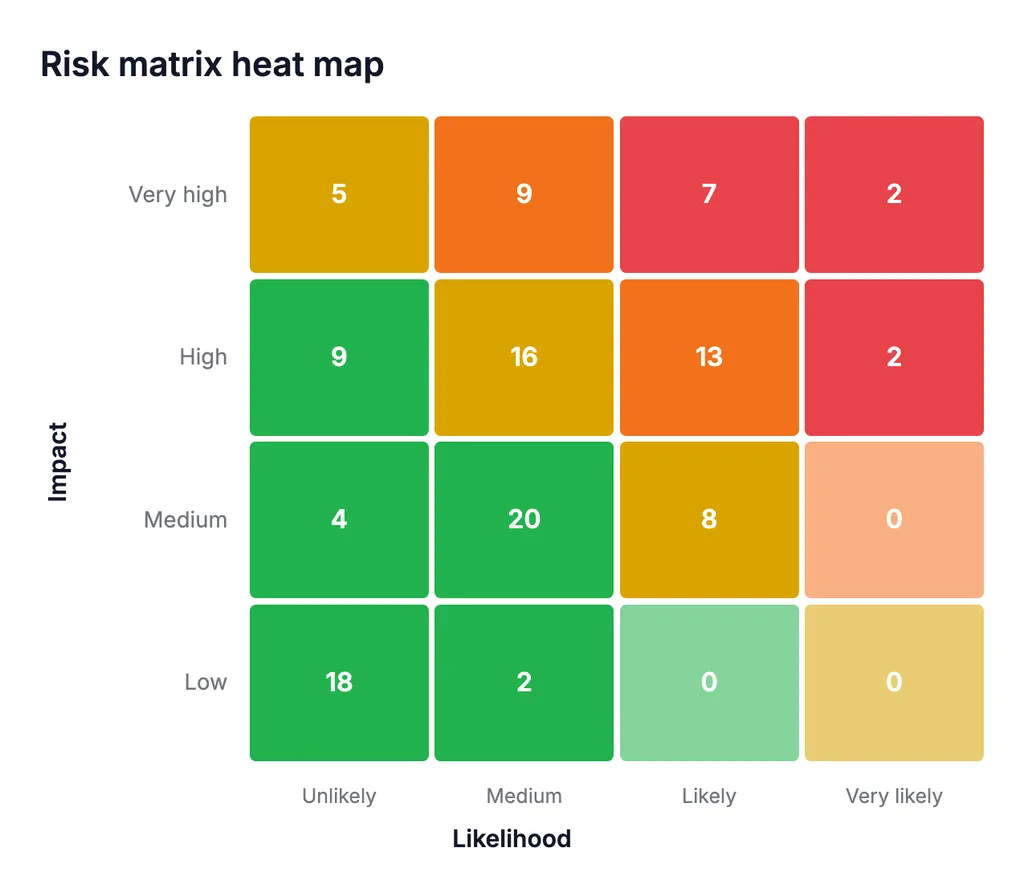
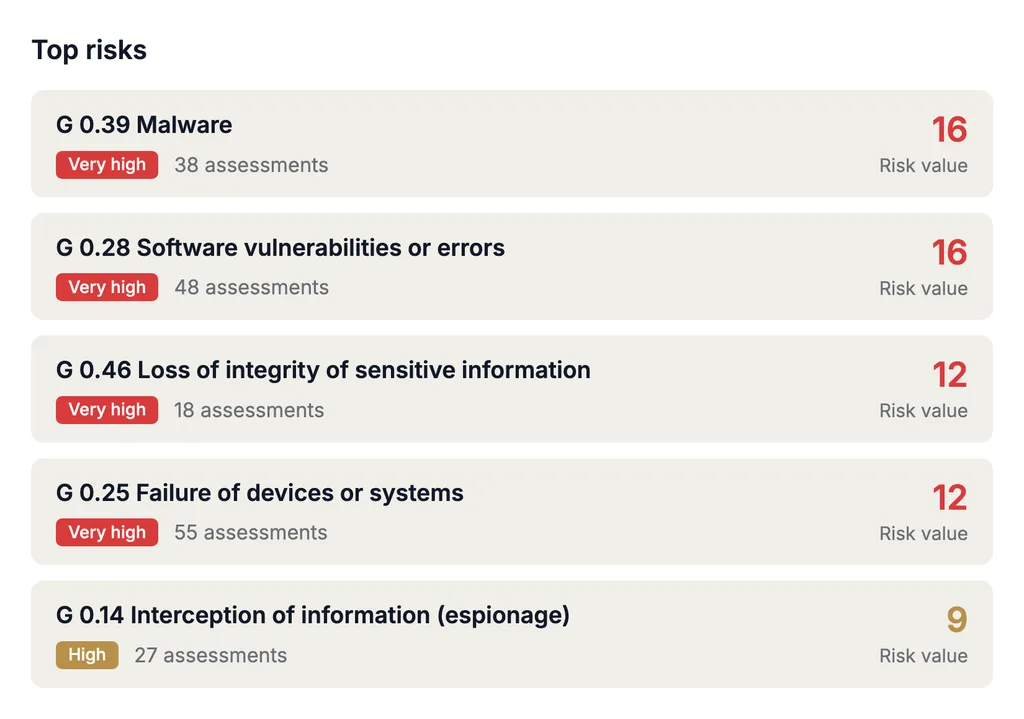
Risk analysis, risk assessment and risk treatment
Identify threats per asset — from standard or your own threat catalogues — and assess likelihood and impact in a configurable risk matrix. For every risk the treatment option is set, linked to controls and measures, and the residual risk is tracked over time. Complaica supports risk identification, analysis, evaluation and treatment as the structured process ISO/IEC 27005 describes for information security.
05 / 07 · Reporting & data analysis
Reports for management, risk treatment and audit
Generate the Statement of Applicability, risk treatment plan, implementation status and risk reports from your own data — as a report template per standard or as a custom report. Dashboards show management the state of the ISMS; distribution is handled by the Complaica Teams integration and the mail bot, and external BI and data analysis tools read the data over the REST API or data marts.
06 / 07 · Task management & collaboration
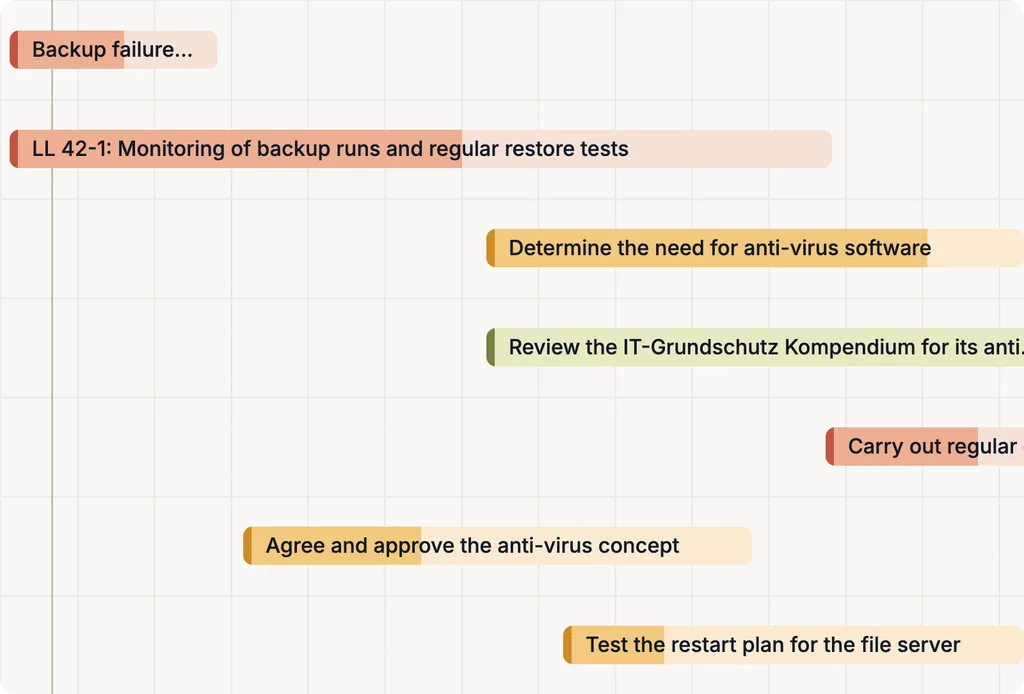
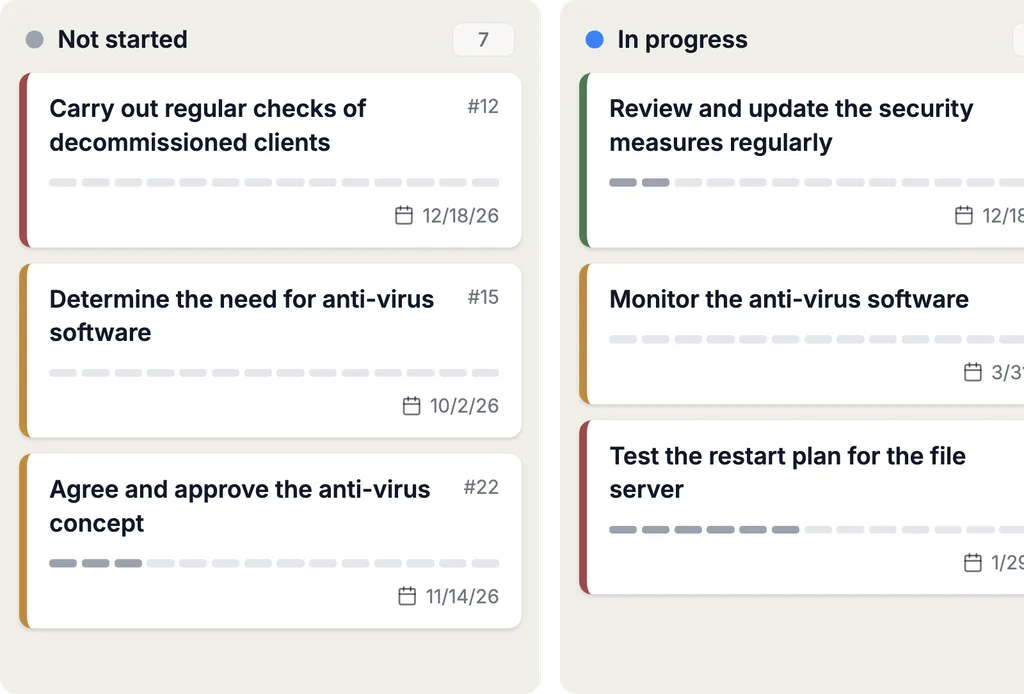
Measures, owners and deadlines
Measures and tasks carry owners, deadlines and status; every status change is recorded with author and date. Internal and external participants — auditors or service providers, say — work in the same system: access to individual assets and documents is granted per object and by link.
07 / 07 · Integrations & automation
Complaica integrations
Over the REST API Complaica connects asset management and CMDB systems — Microsoft Azure, i-doit, GLPI, FNT Command and others — and keeps the asset inventory in the ISMS in step with reality. Jira, Microsoft Planner and others can be connected as task systems.
Application data is available through preset data marts, the REST API or MCP for external analysis and reporting systems.
Complaica ISO 27001 tool: from risk to audit
One connected data set: every object points to the next — from business process and asset to the audit evidence.
- 01
Assets
Processes, systems and data in the ISMS scope, with their dependencies.
- 02
Risks
Identify threats per asset and assess them in the risk matrix — aligned with ISO/IEC 27005.
- 03
Risk treatment
Set the treatment option — avoid, reduce, transfer, accept — and document the residual risk.
- 04
Annex A controls
Select and assess the relevant controls and link them to risks, assets and measures.
- 05
Measures
Track implementation with owners, deadlines and status.
- 06
Evidence
Store documents and assessments on the object, with author and date.
- 07
SoAStatement of Applicability
Justify the applicability of the Annex A controls and document their implementation status.
- 08
Audit
Reports and evidence for internal audit, certification audit and surveillance audits.
Why Complaica as ISO 27001 ISMS software?
Six reasons organisations build and run their ISMS with Complaica.
Software plus expert consulting
ISMS software and consulting from one source: our compliance experts accompany setup, operation and audit preparation — as far as you need.
ISO 27001 ready to use — with 27002 and 27005
The requirements of ISO/IEC 27001:2022 for the ISMS, the 93 Annex A controls with implementation guidance from ISO/IEC 27002:2022, a risk management process aligned with ISO/IEC 27005, report templates and guides are prepared. You do not start from zero.
One connected data set instead of Excel, PowerPoint and shared folders
Assets, risks, controls, measures and evidence stay connected in one data model — instead of being scattered across spreadsheets, presentations and shared folders and kept consistent by hand.
Integrations, API and reporting
CMDB and asset management systems, Jira, SAP and Microsoft Azure over the REST API; reports, dashboards, AI and data marts for management and auditors.
From the first audit to recertification
One data set for initial certification, surveillance audits and recertification: the state of the ISMS stays current between audits, nothing is rebuilt.
Streamline compliance tasks with AI assistance
With the optional AI integration (MCP), Complaica answers questions on ISO/IEC 27001 and 27002, explains requirements and controls, helps with measures and tasks and finds answers in your own policies and documents. It supports the work in the ISMS — assessment and decision stay with you.
- 01Answer questions on ISO/IEC 27001 and ISO/IEC 27002
- 02Explain requirements and Annex A controls — what is required and what counts as evidence
- 03Suggest, formulate and assign measures and tasks
- 04Analyse your policies, procedures and documents and answer questions about them
- 05Explain how to use Complaica — which function for what
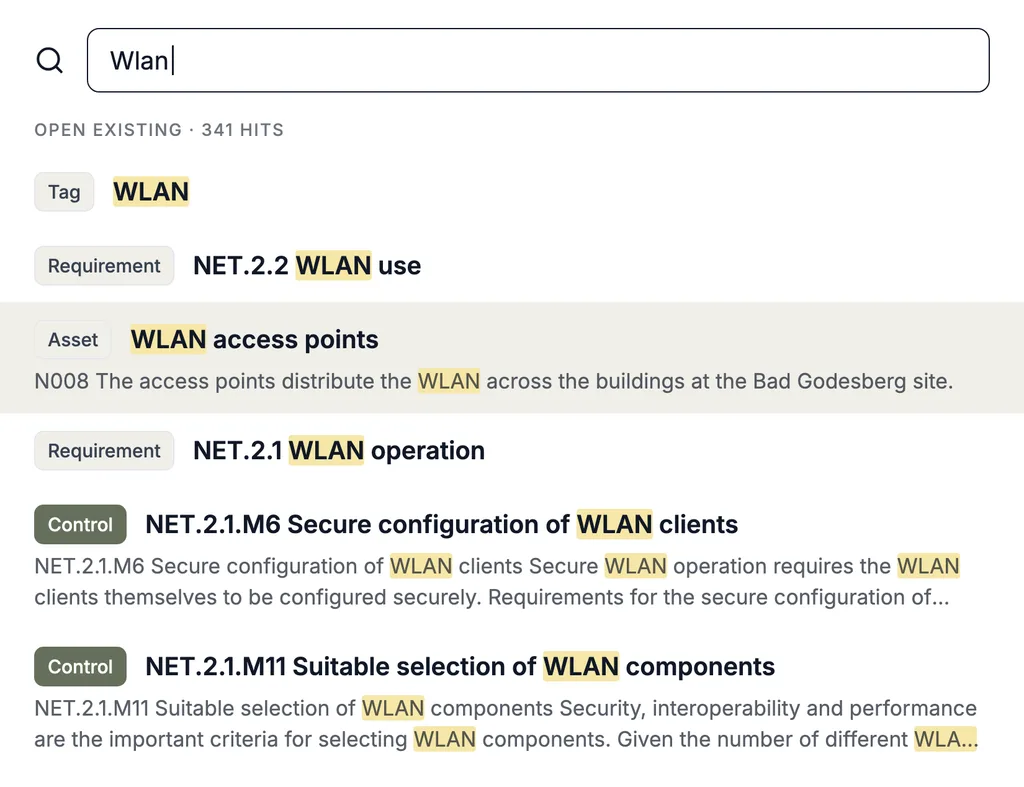
Customer voices on the ISO 27001 ISMS with Complaica
“We can do everything we need in one tool”
Complaica is extremely user-friendly and customising it is child’s play. We can take care of ISO compliance and data protection with it — we can do everything we need in one tool. For us, Complaica is better than the alternatives on the market and cheaper at the same time.
More …Less
Complaica is extremely user-friendly and customising it is child’s play. We can take care of ISO compliance and data protection with it — we can do everything we need in one tool.
For us, Complaica is better than the alternatives on the market and cheaper at the same time.
“The optimised compliance process”
One of the features we like best about Complaica is the optimised compliance process. The user interface has a clear, structured design that offers more usability and encourages a higher working speed. This not only gives new users a steep learning curve, it also lets experienced users minimise their effort. In every phase of the security management lifecycle, recurring tasks such as scoping, structure analysis, modelling and even the tracking of risks and measures are supported by a wealth of functionality. On top of that the platform’s performance is great — it is stable and excellent in terms of speed.
More …Less
One of the features we like best about Complaica is the optimised compliance process. The user interface has a clear, structured design that offers more usability and encourages a higher working speed. This not only gives new users a steep learning curve, it also lets experienced users minimise their effort.
In every phase of the security management lifecycle, recurring tasks such as scoping, structure analysis, modelling and even the tracking of risks and measures are supported by a wealth of functionality.
On top of that the platform’s performance is great — it is stable and excellent in terms of speed.
“The guided approach played a decisive role for us”
We were new to compliance and to implementing ISO 27001, and had to go through the complicated certification process. Given the regulatory complexity, we wanted to find the best way for us to get started. Our project manager (aka security officer) had never worked with such compliance standards and rules before. So we decided on support from a third party — Complaica, to be precise. The guided approach played a decisive role for us. Complaica had all the detailed explanations for the compliance check and the risk analysis, including practical suggestions.
More …Less
We were new to compliance and to implementing ISO 27001, and had to go through the complicated certification process.
Given the regulatory complexity, we wanted to find the best way for us to get started. Our project manager (aka security officer) had never worked with such compliance standards and rules before.
So we decided on support from a third party — Complaica, to be precise. The guided approach played a decisive role for us. Complaica had all the detailed explanations for the compliance check and the risk analysis, including practical suggestions.
Information security as a service
Consulting along the ISO 27001 lifecycle — from gap analysis to audit preparation, to the extent you need.
- Gap analysis and preparation
Comparison of your current state with the requirements of ISO/IEC 27001:2022 and the Annex A controls. Result: a prioritised list of gaps and an implementation plan.
- Setup and introduction of the ISMS
Scope, organisation, asset structure and roles are set up in Complaica. You get a working ISMS with the processes the standard requires.
- Risk management and measure planning
Define the risk methodology and risk matrix with reference to ISO/IEC 27005, identify, analyse and evaluate risks, choose treatment options and derive the risk treatment plan.
- Policies and documented information
Creation, review and maintenance of information security policies, procedures and the documented information ISO 27001 requires.
- Internal audits and audit preparation
Internal audits per clause 9.2, management review and preparation for the certification audit — including the evidence the auditor wants to see.
- External information security officer
A contact for your ISMS, for a time or permanently — for organisations without a role of their own for it.
Other supported standards
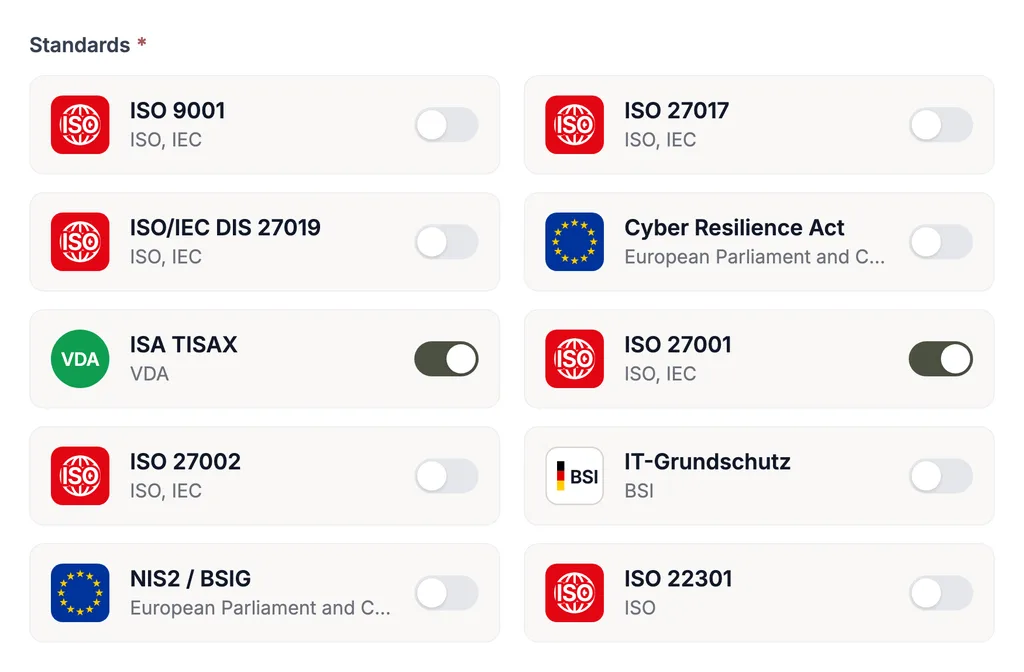
ISO 27001 is rarely the only standard that applies to an organisation. In Complaica the requirements of further standards use the same assets, risks, measures and evidence: what is documented for ISO 27001 also counts for NIS2, DORA, TISAX, IT-Grundschutz or the GDPR. No duplicate maintenance.
Every standard ships with its requirement catalogue; your own catalogues can be added at any time.
Frequently asked questions
What is ISO 27001?
ISO/IEC 27001 is the internationally recognised standard for information security management systems (ISMS). It defines how an organisation plans, implements, monitors and improves information security systematically — with risk assessment at its core and the 93 controls of Annex A as its catalogue of measures; ISO/IEC 27002:2022 gives implementation guidance for them. The current edition is ISO/IEC 27001:2022.
What is ISMS software?
ISMS software maps the components of an information security management system in one data model — scope, assets, requirements, risks, controls and evidence — and links them to each other. Instead of keeping spreadsheets and documents consistent by hand, you maintain every object once, and reports such as the Statement of Applicability are generated from the data.
Which functions should ISO 27001 software offer?
At least: the requirements of ISO/IEC 27001:2022 and the Annex A controls with implementation status, an asset structure with dependencies, risk analysis and risk treatment with a configurable risk matrix, measures with owners and deadlines, evidence on the object, the Statement of Applicability, reports for management review and audit — and interfaces to the systems where your assets and tasks already live.
Does Complaica support ISO/IEC 27001:2022 and ISO/IEC 27002?
Yes. The requirements of ISO/IEC 27001:2022 and the 93 Annex A controls of the standard are included as a catalogue — with implementation guidance from ISO/IEC 27002:2022 — and are assessed on your asset tree. When a new edition of the standard appears, the catalogue is updated; existing assessments and evidence migrate with it.
Does Complaica support creating and maintaining a Statement of Applicability (SoA)?
Yes. The SoA is built on the basis of the requirements and controls: for every control, applicability, justification and implementation status are documented, and the report is generated from that — at the initial audit and before every surveillance audit, without rewriting the statement.
How does Complaica support ISO 27001 risk management?
Threats are identified per asset — from standard or your own threat catalogues — and assessed in a configurable risk matrix. For every risk, the treatment option and measures are set; gross and residual risk can be tracked over time, and the risk treatment plan is generated as a report.
Does Complaica support risk management according to ISO/IEC 27005?
Yes — as guidance, not as a certification standard: ISO/IEC 27005 describes the information security risk management process that ISO/IEC 27001 requires. Complaica maps that process: risks are identified, analysed and evaluated per asset, for every risk the treatment option, controls and measures are set, and the residual risk stays linked to asset, risk and evidence. There is no certification against ISO/IEC 27005; the results feed the risk treatment plan and the SoA for the ISO 27001 audit.
Can an existing ISMS be taken over from Excel or other systems?
Yes. Complaica imports and exports data from and to Excel, over the REST API and from other ISMS tools; migrating your data is free and accompanied by our specialists. So you evaluate the tool on your own data set rather than on demo data.
Can Complaica manage several standards at once?
Yes. TISAX, BSI IT-Grundschutz, NIS2, GDPR, ISO 22301 and further standards are assessed on the same scope model and use the same assets, risks, measures and evidence. What is documented for ISO 27001 counts for the other standards too.
Is Complaica available as SaaS and on-premises?
Yes, both. The SaaS variant is hosted in Germany; on-premises you run Complaica in your own infrastructure. The licence costs the same either way.
Which systems can be integrated with Complaica?
Over the REST API, asset management and CMDB systems such as i-doit, GLPI, FNT Command and others, as well as Jira, SAP and Microsoft Azure. Application data is available through data marts for external analysis and reporting systems, and an AI assistant can be connected over MCP.
How does Complaica support audits, surveillance audits and recertification?
Evidence sits on the object it proves, and the reports — SoA, risk treatment plan, implementation status — are generated from the current data set. Dashboards show the state before the audit, and external auditors can be given targeted access. Because the same data set keeps running, surveillance audits and the recertification after three years are prepared out of ongoing operation. The certification itself is performed by an independent certification body.
Who is ISO 27001 certification suitable for?
For any organisation that processes confidential information and wants to prove it to customers, partners or regulators — regardless of size and industry. It is especially common among IT and cloud service providers, suppliers to regulated industries, operators of critical infrastructure and companies facing NIS2 or TISAX: an ISMS according to ISO 27001 covers a large part of those requirements too.
Is ISO 27001 certification mandatory?
It is not required by law. In practice it becomes mandatory through contracts and tenders — many customers demand the certificate as proof — and indirectly through regulations such as NIS2, KRITIS or DORA that require an ISMS; ISO 27001 is the usual way to run that ISMS demonstrably.
How much does ISO 27001 certification cost?
The costs have three parts: the effort for setting up and running the ISMS (internal time, consulting, software), the certification audit by an accredited body and the annual surveillance audits. They depend above all on the size of the scope, the number of sites and the maturity of your existing processes. Complaica lowers the first part: the prepared content, the evidence generated from the data and the AI integration save most of the documentation work. We send you a price list on request.
How long does it take to obtain ISO 27001 certification?
Typically three to twelve months from start to certificate — depending on scope, existing documentation and available resources. With prepared content and consulting, smaller organisations sit at the lower end. The certificate is valid for three years, with annual surveillance audits and recertification afterwards — Complaica keeps the data set current throughout.
Start ISO 27001 with Complaica
Test Complaica, request a demo or talk about your existing ISMS and a migration — write to us.
Thank you.
We will get back to you within one business day.
Not sent.
That did not work. Please check the fields or email us directly.