NIS2 Software
for compliance and risk management
Complaica is NIS2 software with which organisations manage and document their NIS2 implementation and provide the evidence for it: the NIS2 requirements under the BSIG, risk management and measures, security incidents with their reporting deadlines, and the evidence towards management and the supervisory authority. Unlike an NIS2 checklist, Complaica connects requirements, assets, risks, measures and evidence in one data set — from it, dashboards show the level of fulfilment, with AI integration.
- 01NIS2 compliance from scope to evidence — in one data set
- 02NIS2 requirements under the BSIG, plus Implementing Regulation (EU) 2024/2690 for the types of entity it covers
- 03Dashboards with the level of fulfilment of the requirements, cumulated up to the organisation
- 04Risks, measures, security incidents and evidence managed centrally
- 05AI integration (MCP) plus expert consulting — Co-Intelligence
Implement and manage NIS2 with Complaica
Functions with which Complaica, as software for NIS2 implementation, covers the path from the NIS2 requirements to the evidence.
- 01Assess the requirements of NIS2 — the ten risk management measures under § 30 BSIG with implementation level per requirement, cumulated up to the top level
- 02Implementing Regulation (EU) 2024/2690 as a catalogue for the types of entity it covers: Art. 1–14 and the 13 subject areas of the Annex
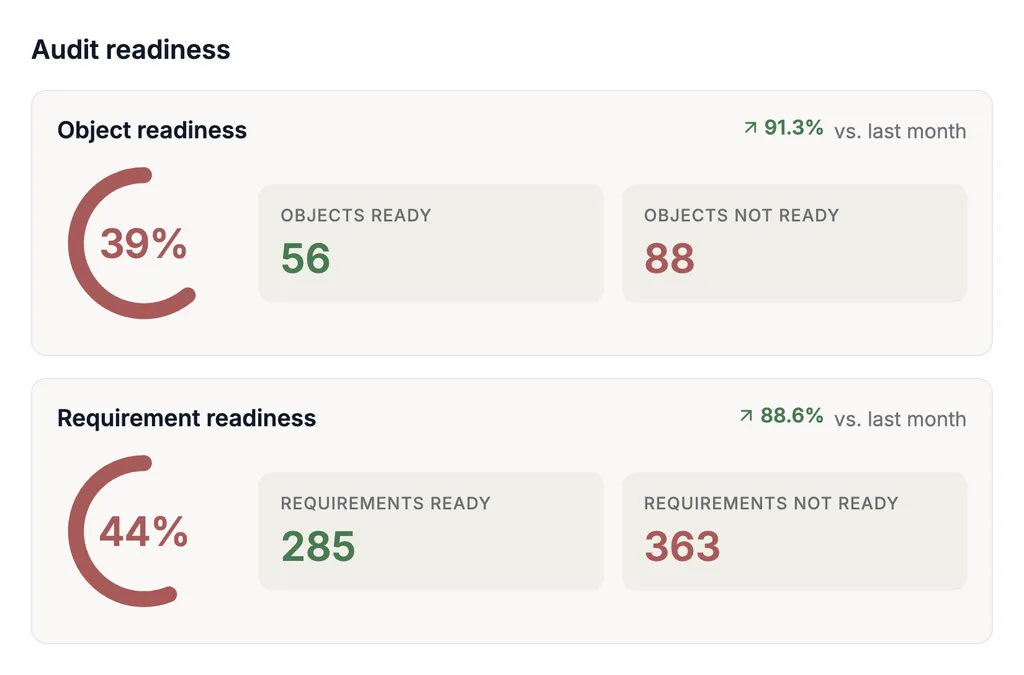
- 03Dashboards for the summary assessment: the level of fulfilment per requirement, per subject area and for the whole organisation
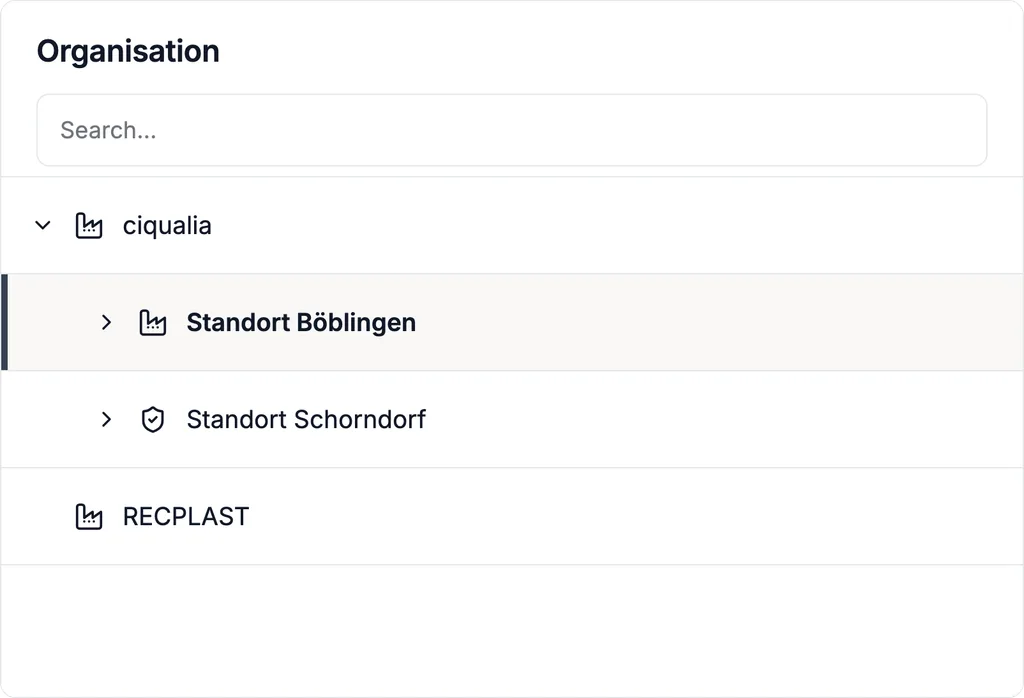
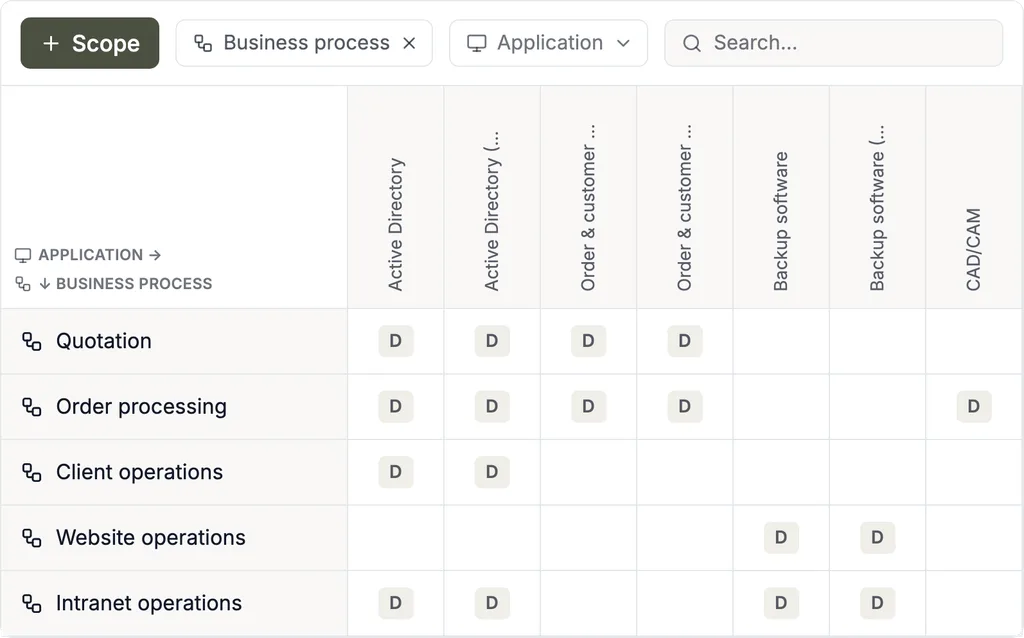
- 04Map the scope and asset structure — organisation, business processes, systems, service providers and their dependencies
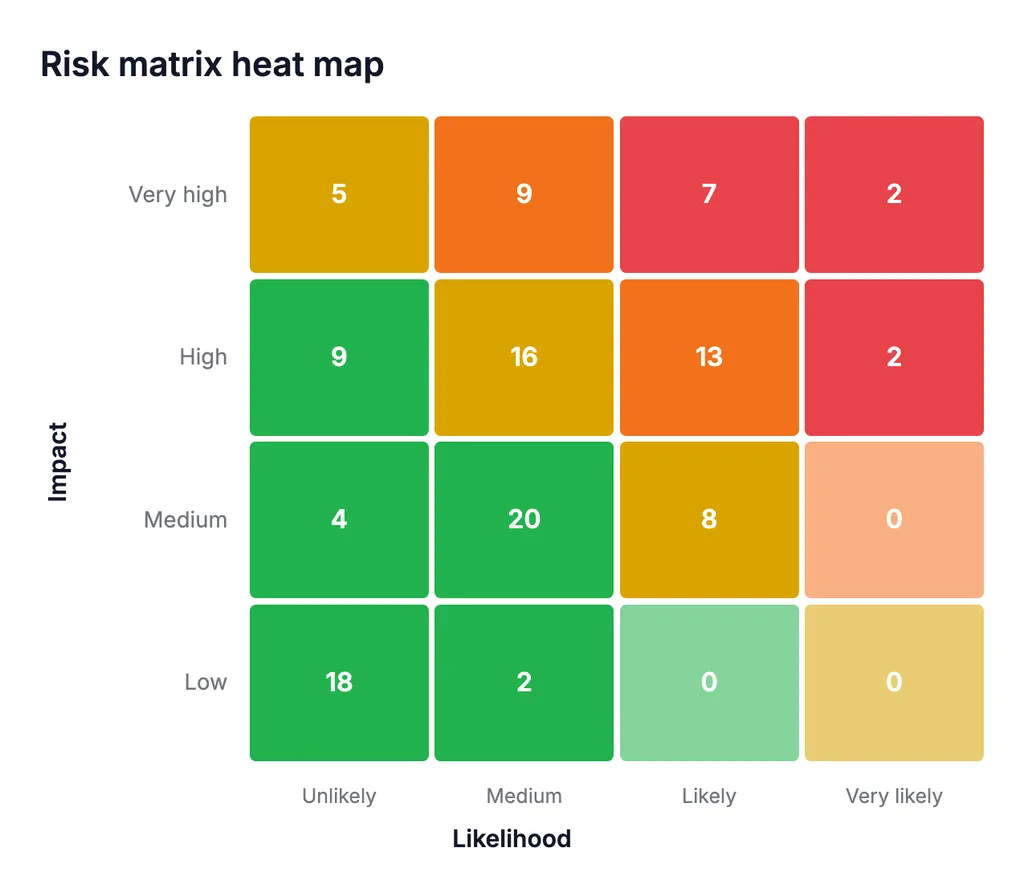
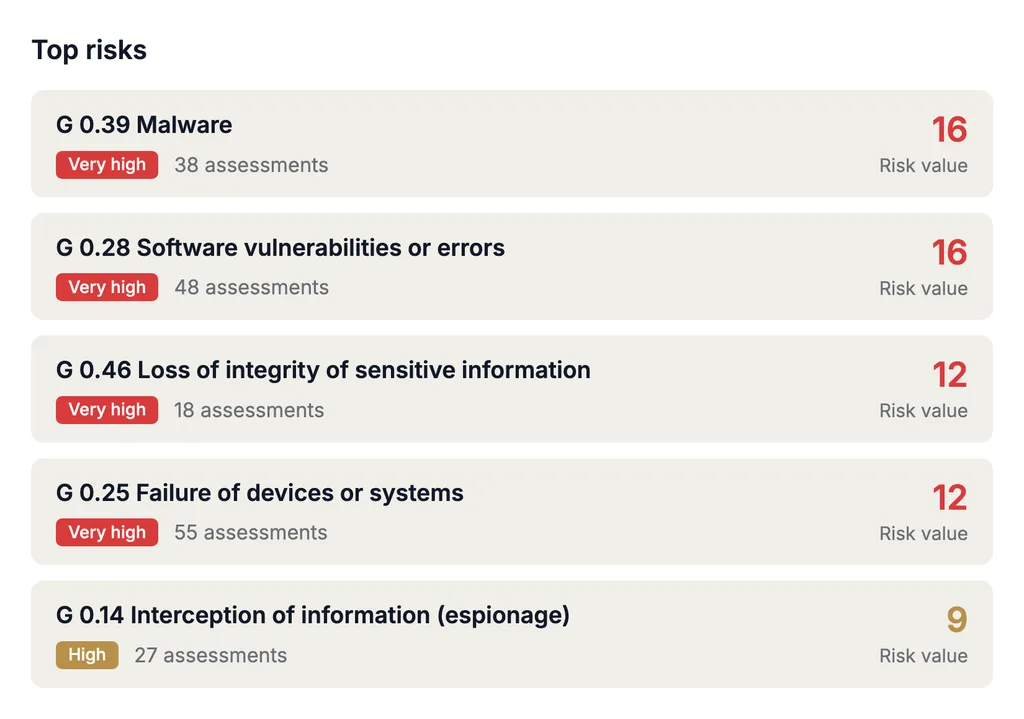
- 05Identify risks per asset and assess them in configurable risk matrices
- 06Plan risk treatment — treatment option, measures and residual risk documented traceably
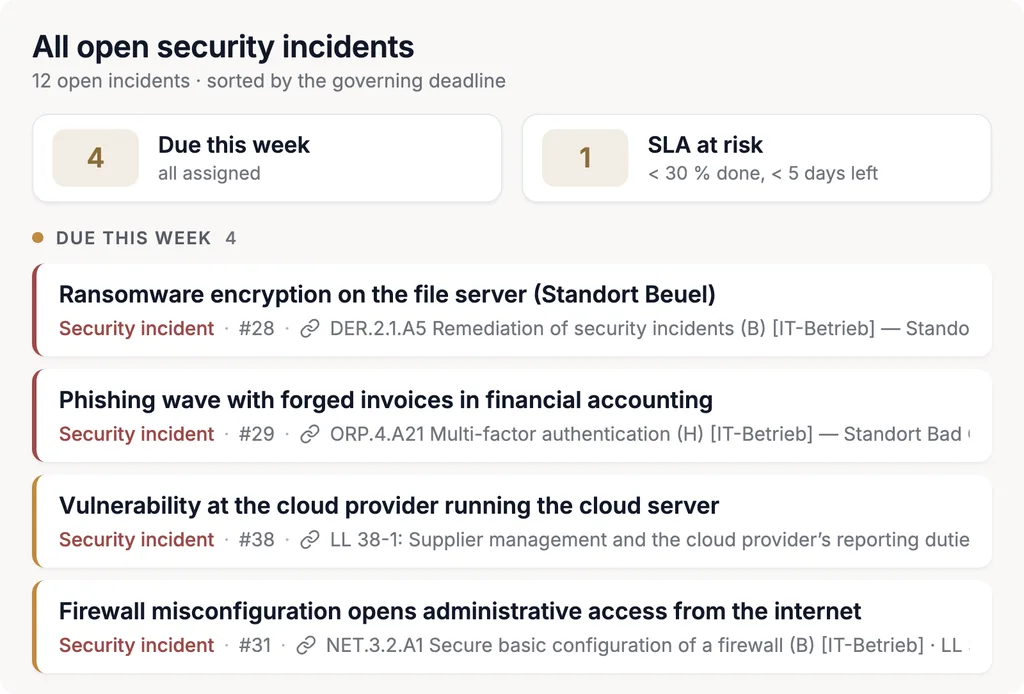
- 07Manage security incidents with deadlines and owners — 24 hours, 72 hours, final report
- 08The supply chain in view: service providers as assets, with their own requirements, risks and evidence
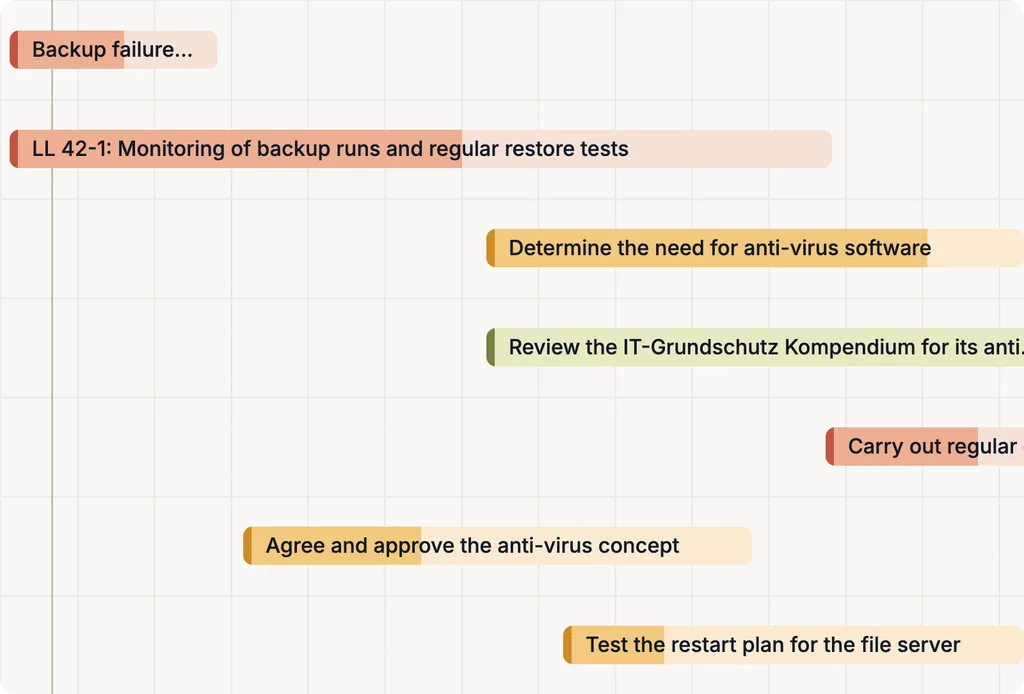
- 09Track measures with owners, deadlines and status; store evidence on the object it belongs to
- 10Reports for management, internal audit and the supervisory authority
- 11Integration with Microsoft Azure, SAP, Jira and further systems; import and export from and to Excel
- 12AI integration (MCP) for questions on NIS2, requirements and measures, and on using the tool
Manage NIS2 requirements and Regulation (EU) 2024/2690 centrally
Implementing Regulation (EU) 2024/2690 spells out what the NIS2 Directive requires in Art. 21 and Art. 23: technical and methodological requirements for the risk management measures and the criteria for when a security incident counts as significant. It applies directly to certain types of digital entity: DNS service providers and TLD name registries, cloud computing service providers and data centre service providers, content delivery network (CDN) providers, managed service providers and managed security service providers, providers of online marketplaces, of online search engines and of social networking services platforms, and trust service providers. For these types of entity, Complaica contains the regulation as a requirement catalogue — Art. 1–14 and the Annex — and assesses it on the same data set as § 30 BSIG.
This page covers NIS2 implementation within the German legal framework: the NIS2 implementation act (German: NIS2-Umsetzungsgesetz) has anchored the duties in the BSIG — § 30 BSIG for the risk management measures, § 32 BSIG for the reporting duties, § 38 BSIG for management.
- 01 Policy on the security of network and information systems
- 02 Risk management policy
- 03 Incident handling
- 04 Business continuity and crisis management
- 05 Supply chain security
- 06 Security in network and information systems acquisition, development and maintenance
- 07 Policies and procedures to assess the effectiveness of risk-management measures
- 08 Basic cyber hygiene practices and security training
- 09 Cryptography
- 10 Human resources security
- 11 Access control
- 12 Asset management
- 13 Environmental and physical security
NIS2 risk management under § 30 BSIG
Complaica supports risk management and the risk management measures under NIS2 and § 30 BSIG. The law requires appropriate, proportionate and effective technical and organisational measures — in line with the state of the art and based on an all-hazards approach — and that compliance with them is documented.
In Complaica this is one continuous process: risk analysis per asset, risk assessment in the configurable risk matrix, risk treatment with measures and owners, the residual risk over time. The assessment of effectiveness rests on the implementation status and the evidence stored on every measure.
The ten risk management measures under § 30(2) BSIG
- 01Policies on risk analysis and information system security
- 02Incident handling
- 03Business continuity — backup management, disaster recovery, crisis management
- 04Supply chain security
- 05Security in acquisition, development and maintenance, including vulnerability handling and disclosure
- 06Assessment of the effectiveness of the risk management measures
- 07Training and awareness-raising measures
- 08Use of cryptography
- 09Human resources security, access control and the management of ICT systems
- 10Multi-factor authentication and secured communications
NIS2 reporting duties and security incidents under § 32 BSIG
A significant security incident triggers the NIS2 reporting duty: § 32 BSIG requires it to be reported to the joint reporting office of BSI and BBK within fixed deadlines. Complaica manages every NIS2 security incident as a record of its own — with timestamps, owners and the affected assets — and the reporting deadlines run alongside as due dates.
This keeps incident management traceable: every step is recorded with author and date, and measures arising from the incident are tracked like all others. You submit the report itself to the reporting office.
Reporting deadlines under § 32 BSIG
- 24 hours · early warning
Without undue delay, and at the latest 24 hours after becoming aware of a significant security incident.
- 72 hours · notification
Confirms or updates the information given in the early warning.
- On request · intermediate report
Status updates when the BSI requests them.
- One month · final report
No later than one month after the notification. If the incident is still ongoing, a progress report takes its place.
Supply chain security under NIS2
Supply chain security is one of the risk management measures of § 30 BSIG — including the relationships with direct suppliers and service providers. In Complaica, service providers and suppliers sit in the same model as your own assets: supplier risks are assessed where the dependency exists.
For NIS2 supply chain security, Complaica thus uses the same functions as for the rest of the scope — requirements, risks, measures and evidence.
The supply chain in Complaica
- Service providers as assets
Suppliers and service providers are recorded with type and attributes — like applications, systems and sites.
- Dependencies made visible
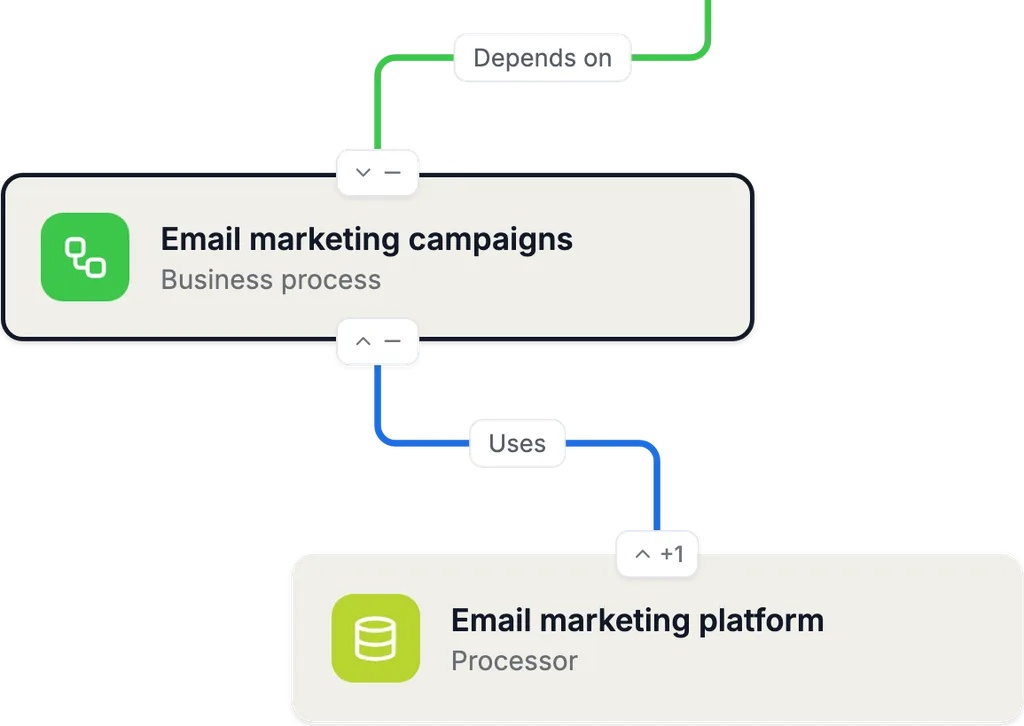
Dependency graph and matrix show which business process and which service depends on which provider.
- Requirements and supplier risks
Per service provider, requirements are assessed and risks are identified, assessed and treated.
- Evidence on the service provider
Documents, links and assessments are stored on the object, with author and date.
NIS2 for management and information security
Under § 38 BSIG, management must implement the risk management measures and oversee their implementation. The dashboards in Complaica give management and the information security officers the overview for this: the implementation status is cumulated from the individual requirement through the subject area up to the organisation and shows how far the NIS2 requirements are implemented — and where the gaps are. The level of fulfilment is an evaluation by Complaica of the implementation status you have assessed, not a metric defined by an authority.
- 01Overall level of fulfilment — one figure for § 30 BSIG and, where it applies, Implementing Regulation (EU) 2024/2690
- 02Breakdown per subject area, per site and per organisational unit
- 03Open and partially implemented requirements with owners and deadlines
- 04Development over time — the state compared with the previous month
- 05View for management: the basis for implementation and oversight under § 38 BSIG
Complaica modules for NIS2 compliance
Modules, one connected data set: organisation, assets, requirements, risks, reports, tasks and integrations work on the same objects.
01 / 07 · Organisation management
Organisation, sites and scope
Map your organisation as a tree — companies, sites, departments, units — and define which parts and services fall under NIS2. Responsibilities are assigned per unit and per object; access rights follow the same structure.
02 / 07 · Asset structure analysis
Assets, dependencies and supply chain
Record assets — applications, systems, data, sites, service providers — with type and further attributes, and link them to the business processes and services that depend on them. Assets can be imported from asset management, CMDBs, Microsoft Azure and other sources.
Service providers and suppliers sit in the same model: the dependency graphs show which service depends on which provider — the basis for the supply chain security NIS2 requires.
03 / 07 · Compliance management
Requirements, implementation status and level of fulfilment
Assess the requirements of NIS2 — § 30 BSIG and, for the types of entity it covers, Implementing Regulation (EU) 2024/2690 — on your asset tree. Every requirement receives an implementation status, a justification and evidence; the status cumulates bottom-up to the organisation.
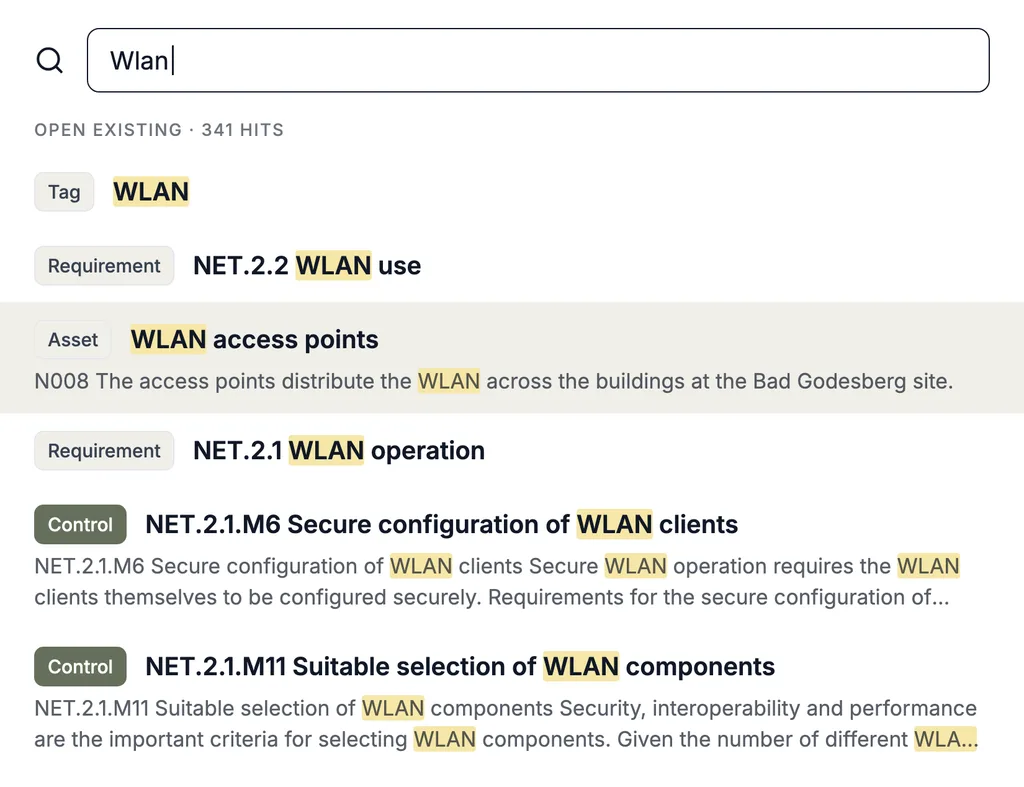
Your own requirement catalogues and further frameworks and standards are assessed on the same model — the same assets, the same evidence. What is already documented for ISO 27001 can — where it fits in substance — also be used for the corresponding NIS2 requirements.
04 / 07 · Risk management
Risk analysis, risk assessment and risk treatment
Identify threats per asset — from standard or your own threat catalogues — and assess likelihood and impact in a configurable risk matrix. For every risk the treatment option is set, linked to measures, and the residual risk is tracked over time — the all-hazards approach NIS2 requires.
05 / 07 · Reporting & data analysis
Reports for management, audit and the supervisory authority
Generate implementation status, risk treatment plan and risk reports from your own data — as a report template per framework or as a custom report. Dashboards show management the current state; distribution is handled by the Complaica Teams integration and the mail bot, and external BI and data analysis tools read the data over the REST API or data marts.
06 / 07 · Task management & collaboration
Measures, security incidents and deadlines
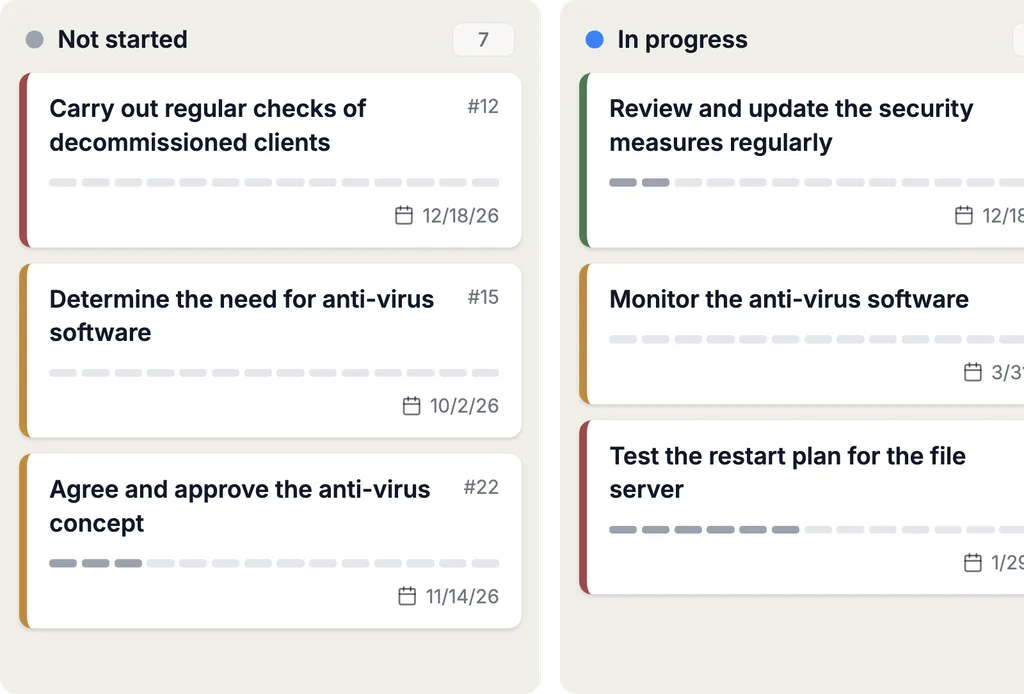
Measures, tasks and security incidents carry owners, deadlines and status; every status change is recorded with author and date. For a security incident, the reporting deadlines run alongside as due dates — 24 hours, 72 hours, final report. Internal and external participants work in the same system: access is granted per object and by link.
07 / 07 · Integrations & automation
Complaica integrations
Over the REST API Complaica connects asset management and CMDB systems — Microsoft Azure, i-doit, GLPI, FNT Command and others — and keeps the asset inventory in step with reality. Jira, Microsoft Planner and others can be connected as task systems.
Application data is available through preset data marts, the REST API or MCP for external analysis and reporting systems.
Complaica NIS2 tool: from risk to evidence
One connected data set: every object points to the next — from scope and asset to the dashboard for management.
- 01
Scope
Organisation, sites and services that fall under NIS2 — with their owners.
- 02
Assets
Processes, systems, data and service providers, with their dependencies.
- 03
Risks
Identify threats per asset and assess them in the risk matrix.
- 04
Requirements§ 30 BSIG · Regulation (EU) 2024/2690
Assess and justify the implementation level per requirement.
- 05
Measures
Track implementation with owners, deadlines and status.
- 06
Evidence
Store documents and assessments on the object, with author and date.
- 07
Security incidentsReporting deadlines under § 32 BSIG
Assess incidents and manage them with deadlines — 24 hours, 72 hours, final report.
- 08
Dashboards
The level of fulfilment as a total — for management, audit and the supervisory authority.
Why Complaica as NIS2 software?
Six reasons companies and organisations use Complaica to implement NIS2 and to provide the evidence.
Software plus expert consulting
ISMS software and consulting from one source: our compliance experts accompany applicability check, implementation and evidence — as far as you need.
NIS2 ready to use — with Regulation (EU) 2024/2690
The risk management measures under § 30 BSIG, Implementing Regulation (EU) 2024/2690 with Art. 1–14 and Annex, report templates and guides are prepared. You do not start from zero.
The level of fulfilment as a single figure
Dashboards cumulate the implementation status from the individual requirement up to the organisation. Management sees where the company stands — without anyone merging spreadsheets.
Integrations, API and reporting
CMDB and asset management systems, Jira, SAP and Microsoft Azure over the REST API; reports, dashboards, AI and data marts for management and auditors.
From the first status to ongoing evidence
One data set for introduction, operation and recurring audits: the state stays current between audits, nothing is rebuilt.
NIS2 compliance with AI assistance
With the optional AI integration (MCP), Complaica answers questions on NIS2, the BSIG and Implementing Regulation (EU) 2024/2690, explains requirements, helps with measures and tasks and finds answers in your own policies and documents. It supports the work in the ISMS — assessment and decision stay with you.
- 01Answer questions on NIS2, the BSIG and Implementing Regulation (EU) 2024/2690
- 02Explain requirements — what is required and what counts as evidence
- 03Suggest, formulate and assign measures and tasks
- 04Analyse your policies, procedures and documents and answer questions about them
- 05Explain how to use Complaica — which function for what
Customer voices on the ISMS with Complaica
“We can do everything we need in one tool”
Complaica is extremely user-friendly and customising it is child’s play. We can take care of ISO compliance and data protection with it — we can do everything we need in one tool. For us, Complaica is better than the alternatives on the market and cheaper at the same time.
More …Less
Complaica is extremely user-friendly and customising it is child’s play. We can take care of ISO compliance and data protection with it — we can do everything we need in one tool.
For us, Complaica is better than the alternatives on the market and cheaper at the same time.
“The optimised compliance process”
One of the features we like best about Complaica is the optimised compliance process. The user interface has a clear, structured design that offers more usability and encourages a higher working speed. This not only gives new users a steep learning curve, it also lets experienced users minimise their effort. In every phase of the security management lifecycle, recurring tasks such as scoping, structure analysis, modelling and even the tracking of risks and measures are supported by a wealth of functionality. On top of that the platform’s performance is great — it is stable and excellent in terms of speed.
More …Less
One of the features we like best about Complaica is the optimised compliance process. The user interface has a clear, structured design that offers more usability and encourages a higher working speed. This not only gives new users a steep learning curve, it also lets experienced users minimise their effort.
In every phase of the security management lifecycle, recurring tasks such as scoping, structure analysis, modelling and even the tracking of risks and measures are supported by a wealth of functionality.
On top of that the platform’s performance is great — it is stable and excellent in terms of speed.
“The guided approach played a decisive role for us”
We were new to compliance and to implementing ISO 27001, and had to go through the complicated certification process. Given the regulatory complexity, we wanted to find the best way for us to get started. Our project manager (aka security officer) had never worked with such compliance standards and rules before. So we decided on support from a third party — Complaica, to be precise. The guided approach played a decisive role for us. Complaica had all the detailed explanations for the compliance check and the risk analysis, including practical suggestions.
More …Less
We were new to compliance and to implementing ISO 27001, and had to go through the complicated certification process.
Given the regulatory complexity, we wanted to find the best way for us to get started. Our project manager (aka security officer) had never worked with such compliance standards and rules before.
So we decided on support from a third party — Complaica, to be precise. The guided approach played a decisive role for us. Complaica had all the detailed explanations for the compliance check and the risk analysis, including practical suggestions.
Consulting for NIS2 implementation
Information security as a service: our experts accompany the NIS2 implementation from the applicability check to the evidence — to the extent you need.
- Applicability check and gap analysis
Does your company fall under NIS2 — and as which type of entity? Then the comparison of your current state with § 30 BSIG and, where it applies, Implementing Regulation (EU) 2024/2690. Result: a prioritised list of gaps and an implementation plan.
- Setup and introduction of the ISMS
Scope, organisation, asset structure and roles are set up in Complaica. You get a working ISMS with the processes NIS2 requires.
- Risk management and measure planning
Define the risk methodology and risk matrix, identify, analyse and evaluate risks, choose treatment options and derive the risk treatment plan.
- Incident management and reporting channels
Process for handling security incidents, assessment of their significance, and the reporting channels for the deadlines of 24 hours, 72 hours and one month.
- Policies, training and management
Creation and maintenance of the policies and guidelines NIS2 requires, and training for employees and management under § 38 BSIG.
- External information security officer
A contact for your ISMS, for a time or permanently — for organisations without a role of their own for it.
Manage NIS2 and ISO 27001 together
NIS2 and ISO 27001 overlap in many organisational and technical topics — risk management, incident handling, supply chain, access control. Complaica manages both sets of rules on the same assets, risks, measures and evidence: what is already documented in the ISMS for ISO 27001 with Complaica can — where it fits in substance — also be used for the corresponding NIS2 requirements. Shared measures and shared evidence save duplicate maintenance. Even so, ISO 27001 certification does not mean that the NIS2 duties are met: registration and the reporting and evidence duties come on top.
The same applies to further supported frameworks and standards — BSI IT-Grundschutz, DORA, TISAX or data protection management under the GDPR. Every framework comes with its requirement catalogue; your own catalogues can be added at any time. More on the compliance platform Complaica and on the ISMS software.
Frequently asked questions about NIS2 software and NIS2 compliance
What is NIS2?
NIS2 is Directive (EU) 2022/2555 on measures for a high common level of cybersecurity across the Union. It obliges important and essential entities to take risk management measures, to report significant security incidents and to register, and it holds management accountable. In Germany the NIS2 implementation act (German: NIS2-Umsetzungsgesetz) has implemented it in the BSI Act (BSIG), which has applied in its new version since 6 December 2025.
What is NIS2 software?
NIS2 software maps the duties of NIS2 in one data model — scope, assets, requirements, risks, measures, security incidents and evidence — and links them to each other. In substance it is ISMS software that comes with the NIS2 requirement catalogue: instead of keeping spreadsheets consistent by hand, you maintain every object once, and reports and dashboards are generated from the data.
How does software support NIS2 implementation?
Software for NIS2 implementation does not replace the work, it puts it in order: the NIS2 requirements are available as a catalogue, and each one is assessed, justified and backed with evidence. Risks and measures are attached to the assets they concern; deadlines and owners are recorded. This way NIS2 compliance can be documented and the state reported at any time — without anyone merging spreadsheets.
Which NIS2 requirements does Complaica support?
Complaica supports the whole NIS2 implementation: the ten risk management measures under § 30 BSIG; for the types of entity it covers, Implementing Regulation (EU) 2024/2690 with Art. 1–14 and the 13 subject areas of its Annex; the management of security incidents with the reporting deadlines under § 32 BSIG; and the view for management under § 38 BSIG. The catalogues are assessed on your asset tree.
Which risk management measures does NIS2 require?
§ 30 BSIG names ten areas that the measures must cover as a minimum: risk analysis and security policies, incident handling, business continuity and crisis management, supply chain security, security in acquisition, development and maintenance, assessment of effectiveness, training, cryptography, human resources security and access control, and multi-factor authentication and secured communications. The measures must be appropriate, proportionate and effective, and compliance with them must be documented.
What does Implementing Regulation (EU) 2024/2690 govern?
It spells out the NIS2 Directive. Art. 1 and 2, together with the Annex, lay down the technical and methodological requirements for the risk management measures; Art. 3 and 4 determine when a security incident counts as significant; Art. 5 to 14 do so for individual types of entity — from DNS service providers through cloud computing and data centre services to trust service providers. The regulation applies directly only to these types of entity.
Which companies does Implementing Regulation (EU) 2024/2690 apply to?
Implementing Regulation (EU) 2024/2690 applies directly only to the types of entity it names itself: DNS service providers, TLD name registries, cloud computing service providers and data centre service providers, content delivery network (CDN) providers, managed service providers and managed security service providers, providers of online marketplaces, of online search engines and of social networking services platforms, and trust service providers. For all other important and essential entities, the duties from the BSIG apply; the regulation can serve them as orientation, but it is not binding on them.
Which reporting duties apply to NIS2 security incidents?
Under § 32 BSIG, significant security incidents must be reported to the joint reporting office of BSI and BBK: with an early warning, a notification and a final report, and additionally with intermediate reports at the request of the BSI. Complaica manages security incidents with timestamps, owners and deadlines and records every step with author and date. You submit the report itself to the reporting office.
What do the 24-hour and 72-hour deadlines under NIS2 mean?
Both deadlines run from the moment the entity becomes aware of a significant security incident. The early warning is due within 24 hours, and within 72 hours the notification, which confirms or updates the initial information. The final report follows no later than one month after that notification; if the incident is still ongoing, a progress report takes its place.
How does Complaica support NIS2 supply chain security?
Service providers and suppliers are managed as assets and linked to the business processes and services that depend on them. Per service provider, requirements can be assessed, supplier risks identified and treated, and evidence stored. Dependency graph and matrix show which service depends on which provider.
What duties does management have under NIS2?
Under § 38 BSIG, management must implement the risk management measures, oversee their implementation and take part in training regularly. Dashboards and reports in Complaica are therefore designed for the management view: the level of fulfilment, the biggest risks and the open measures on one page.
How does Complaica show the level of fulfilment of NIS2?
Every requirement receives an implementation status. Complaica cumulates it bottom-up — from the requirement through the subject area to the organisation — and shows it in dashboards: as an overall value, per subject area, per site and compared with the previous month. The level of fulfilment is an evaluation by Complaica of your own assessments, not a metric defined by an authority.
Who does NIS2 apply to?
Applicability follows from sector, size and activity. Covered are entities in the sectors of Annexes 1 and 2 to the BSIG — such as energy, transport, health, digital infrastructure, ICT services or manufacturing — as a rule from 50 employees or more than 10 million euros in annual turnover and annual balance sheet total; some entities fall under it regardless of their size. We will gladly check with you whether your company is affected.
How are NIS2 and ISO 27001 related?
NIS2 is law, ISO 27001 a standard for the ISMS — in substance the two overlap in many topics, from risk management to access control. In Complaica, NIS2 and ISO 27001 are assessed on the same scope model and use the same assets, risks, measures and evidence. The same goes for TISAX, BSI IT-Grundschutz, DORA, GDPR and ISO 22301: what is already documented can — where it fits in substance — be used for every framework it concerns.
Is ISO 27001 certification enough for NIS2?
It covers a substantial part of the requirements in § 30 BSIG, but replaces neither registration nor the reporting and evidence duties. In Complaica both sets of rules use the same assets, risks, measures and evidence; the gap appears as a list of open requirements.
Is there NIS2 certification for software?
No. NIS2 is a law, not a certification standard: there is neither an NIS2 certificate for entities nor one for software. The entity must implement the measures and be able to prove that at the request of the supervisory authority; whether the duty is met is judged by the competent authority. Complaica keeps the evidence for that ready on the object it proves.
Can Complaica be run on-premises?
Yes. Complaica is available as SaaS and on-premises: the SaaS variant is hosted in Germany; on-premises you run the NIS2 compliance software in your own infrastructure. The licence costs the same either way.
Can an existing ISMS be migrated to Complaica?
Yes. Complaica imports and exports data from and to Excel, over the REST API and from other ISMS tools; migrating your data is free and accompanied by our specialists. So you evaluate the tool on your own data set rather than on demo data.
Which systems can be integrated with Complaica?
Over the REST API, asset management and CMDB systems such as i-doit, GLPI, FNT Command and others, as well as Jira, SAP and Microsoft Azure. Application data is available through data marts for external analysis and reporting systems, and an AI assistant can be connected over MCP.
How long does implementation take?
For a defined scope, the first defensible status reports are typically available after a few weeks — depending on existing documentation and available resources. With prepared content and consulting, smaller organisations sit at the lower end.
Start NIS2 with Complaica
Get to know Complaica as NIS2 software: test it, request a demo or talk about your NIS2 implementation and an existing ISMS — write to us.
Thank you.
We will get back to you within one business day.
Not sent.
That did not work. Please check the fields or email us directly.