IT-Grundschutz Software
for your ISMS
Complaica is IT-Grundschutz software for the setup, operation and continual improvement of an ISMS according to BSI IT-Grundschutz — with every step of the methodology: structure analysis (Strukturanalyse), protection needs determination (Schutzbedarfsfeststellung), modelling (Modellierung), IT-Grundschutz Check, risk analysis (Risikoanalyse) and implementation planning (Realisierungsplanung). The Compendium (Kompendium) is updated regularly, and the migration to Grundschutz++ is prepared.
- 01IT-Grundschutz tool for every step of the methodology — in one data set
- 02Basic, Standard and Core Protection according to BSI-Standard 200-2
- 03IT-Grundschutz Compendium as a catalogue, updated regularly
- 04Ready for the migration to Grundschutz++
- 05AI integration (MCP) plus expert consulting — Co-Intelligence
Implement and manage BSI IT-Grundschutz with Complaica
The functional scope of the IT-Grundschutz software at a glance: from the information domain to the audit evidence, step by step according to BSI-Standard 200-2.
- 01Map the information domain (Informationsverbund) and the scope (Geltungsbereich) — organisation, sites and business processes
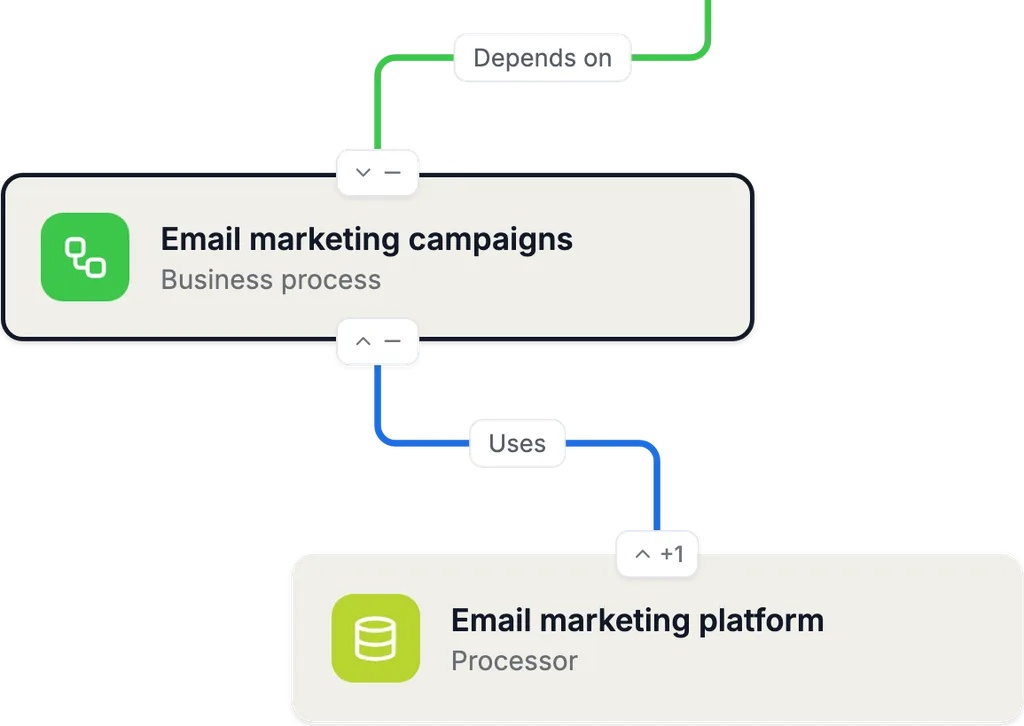
- 02Structure analysis (Strukturanalyse): record and group target objects (Zielobjekte) and show their dependencies as graph and matrix
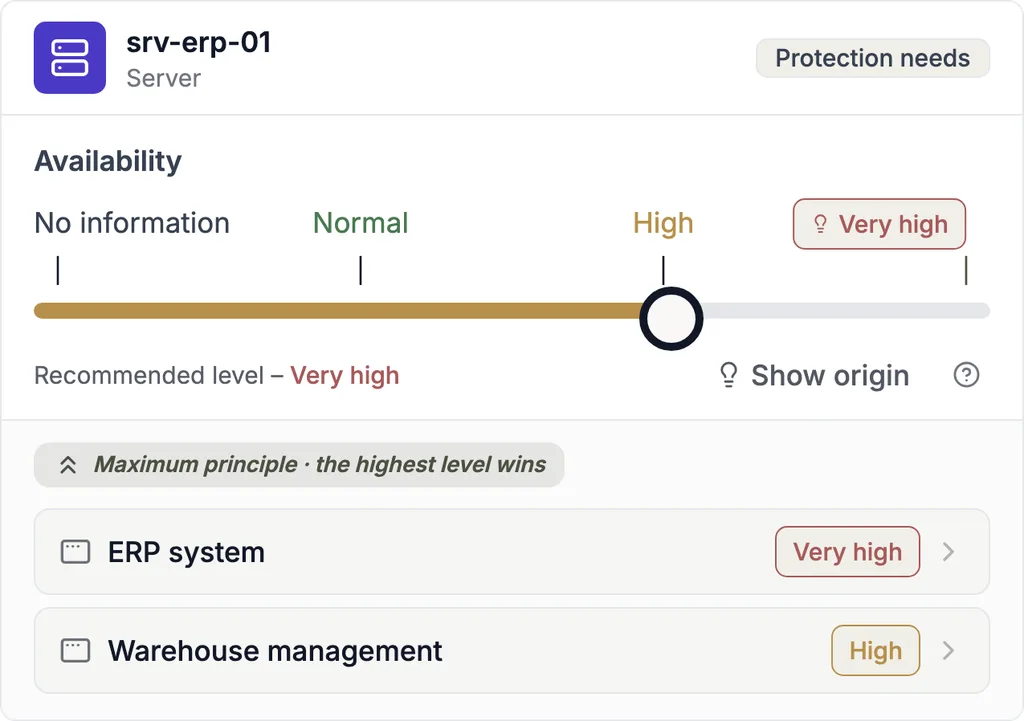
- 03Protection needs determination (Schutzbedarfsfeststellung) for confidentiality, integrity and availability — with inheritance by the maximum principle (Maximumprinzip)
- 04Modelling (Modellierung): assign modules (Bausteine) of the IT-Grundschutz Compendium (IT-Grundschutz-Kompendium) to the target objects
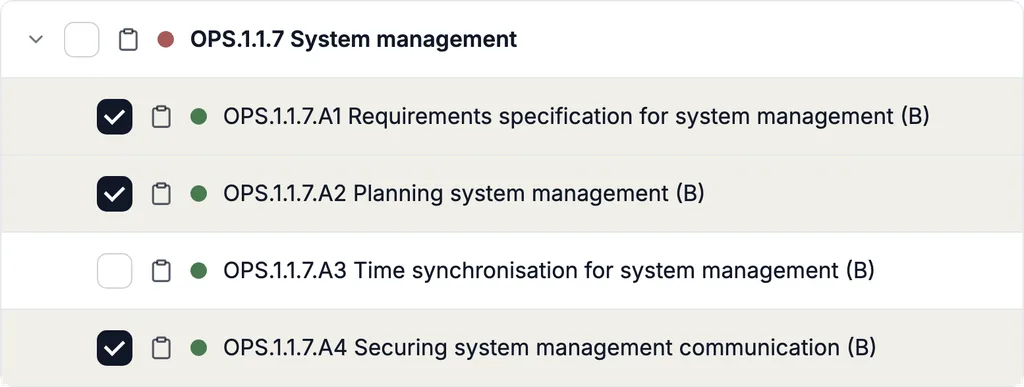
- 05IT-Grundschutz Check: assess the implementation status per requirement, cumulated up to the information domain
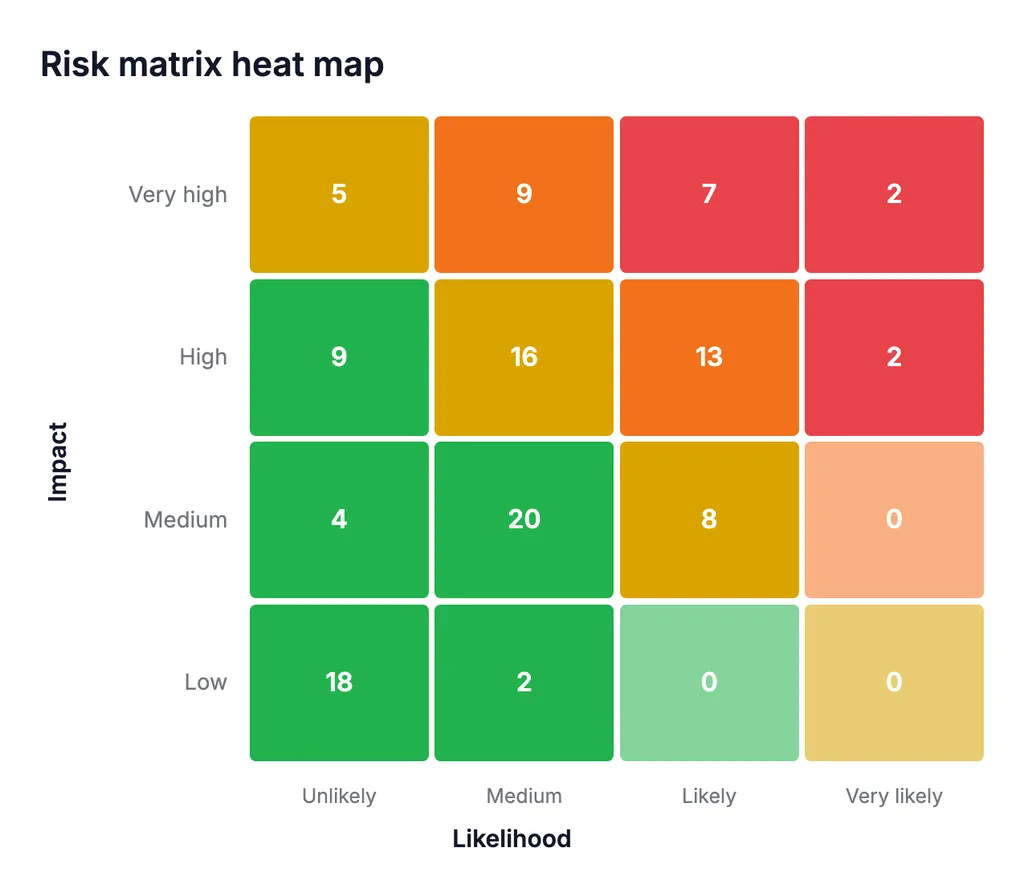
- 06Risk analysis (Risikoanalyse) according to BSI-Standard 200-3 with elementary threats (elementare Gefährdungen) and configurable risk matrices
- 07Implementation plan (Realisierungsplan): track measures with owners, deadlines and status
- 08Store evidence on the object it belongs to — documents, links and assessments with author and date
- 09Reference documents (Referenzdokumente) A.1 to A.6, reports and dashboards for management and audit
- 10Regular updates of the IT-Grundschutz Compendium; Grundschutz++ as a catalogue for the migration
- 11Integration with Microsoft Azure, SAP, Jira and further systems; import and export from and to Excel
- 12AI integration (MCP) for questions on IT-Grundschutz, modules and requirements, and on using the tool
ISMS software for IT-Grundschutz: modules and functions
Seven modules of the ISMS software, one connected data set: information domain, target objects, protection needs, Compendium modules, risks, reports, tasks and integrations work on the same objects.
01 / 07 · Organisation management
Organisation, sites and information domain
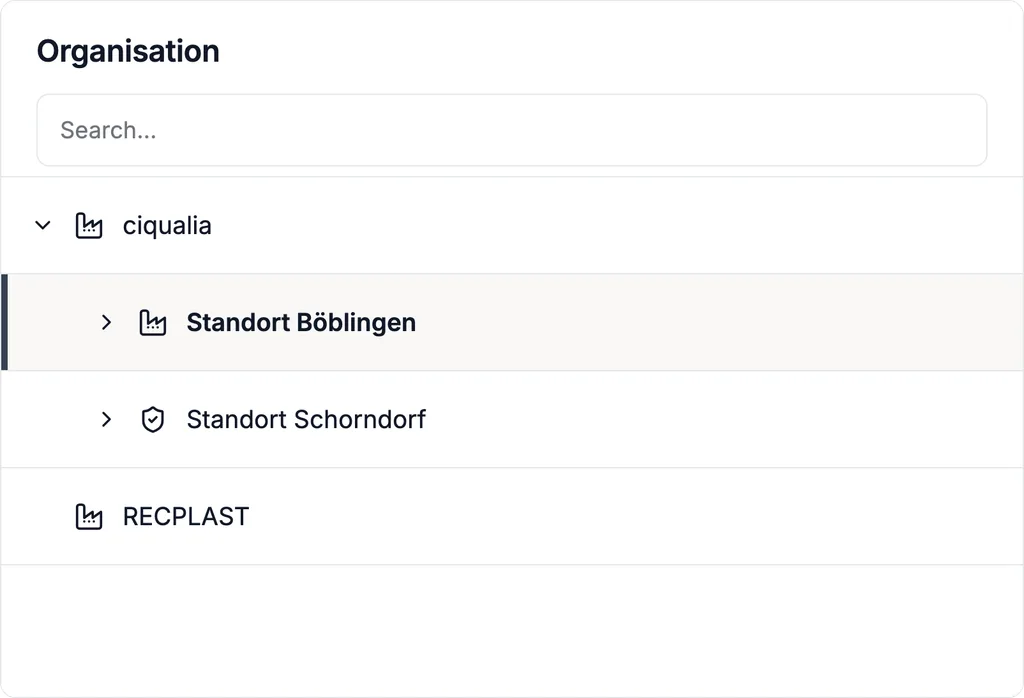
Map your organisation as a tree — entities, sites, departments, units — and define the scope (Geltungsbereich): which parts form the information domain (Informationsverbund). Responsibilities are assigned per unit and per object; access rights follow the same structure.
02 / 07 · Structure analysis & protection needs
Structure analysis and protection needs determination
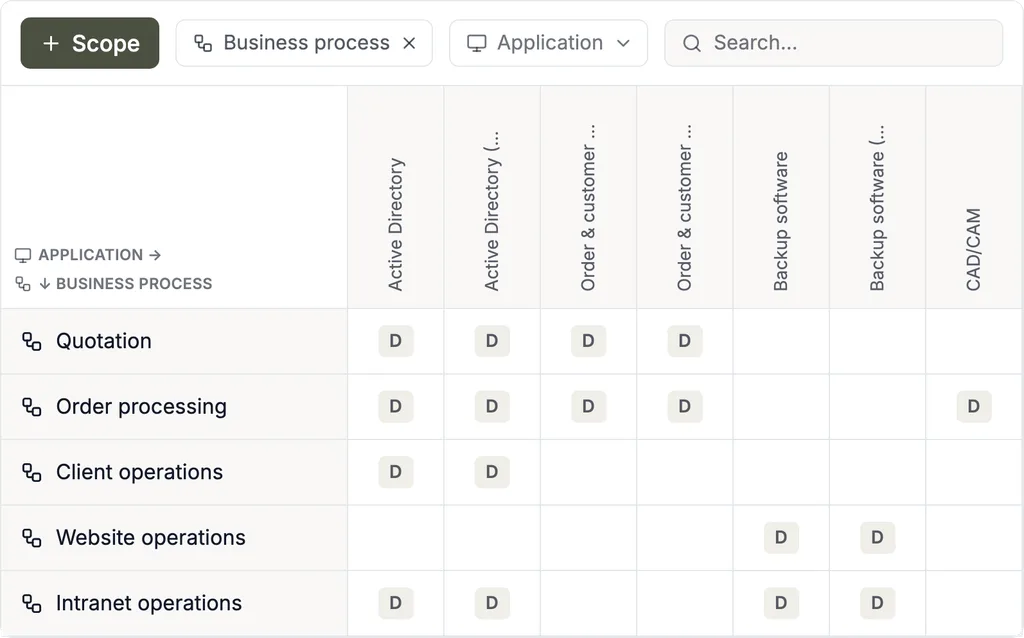
Structure analysis (Strukturanalyse): record the target objects (Zielobjekte) of the information domain — business processes, applications, IT systems, networks, rooms and service providers — with type and further attributes, combine objects of the same kind into groups and link them along their dependencies. Target objects can be imported from asset management, CMDBs, Microsoft Azure and other sources.
Protection needs determination (Schutzbedarfsfeststellung): the protection needs (Schutzbedarf) are determined per target object for confidentiality, integrity and availability — normal, high or very high — and are inherited along the dependencies by the maximum principle (Maximumprinzip). The origin of every rating stays traceable.
03 / 07 · Compliance management
Modelling and IT-Grundschutz Check
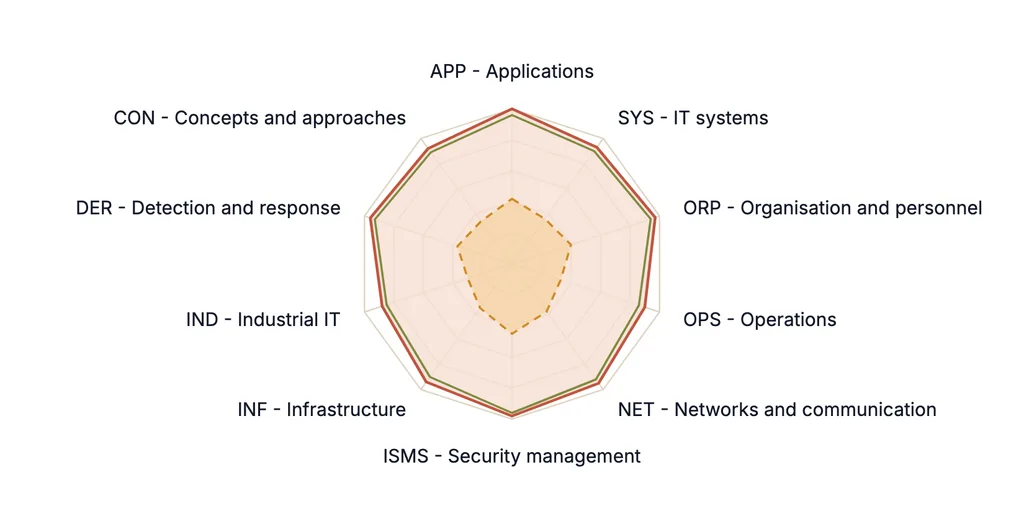
Modelling (Modellierung): assign the modules (Bausteine) of the IT-Grundschutz Compendium (IT-Grundschutz-Kompendium) to the target objects — from all ten layers, from ISMS and ORP to NET and INF. In the IT-Grundschutz Check every requirement receives an implementation status, a justification and evidence; the status cumulates bottom-up to the information domain.
Basic requirements, standard requirements and requirements for increased protection needs can be evaluated separately — so you can begin with Basic Protection (Basis-Absicherung) and extend to Standard Protection (Standard-Absicherung). Your own modules and further standards are assessed on the same model.
04 / 07 · Risk management
Risk analysis according to BSI-Standard 200-3
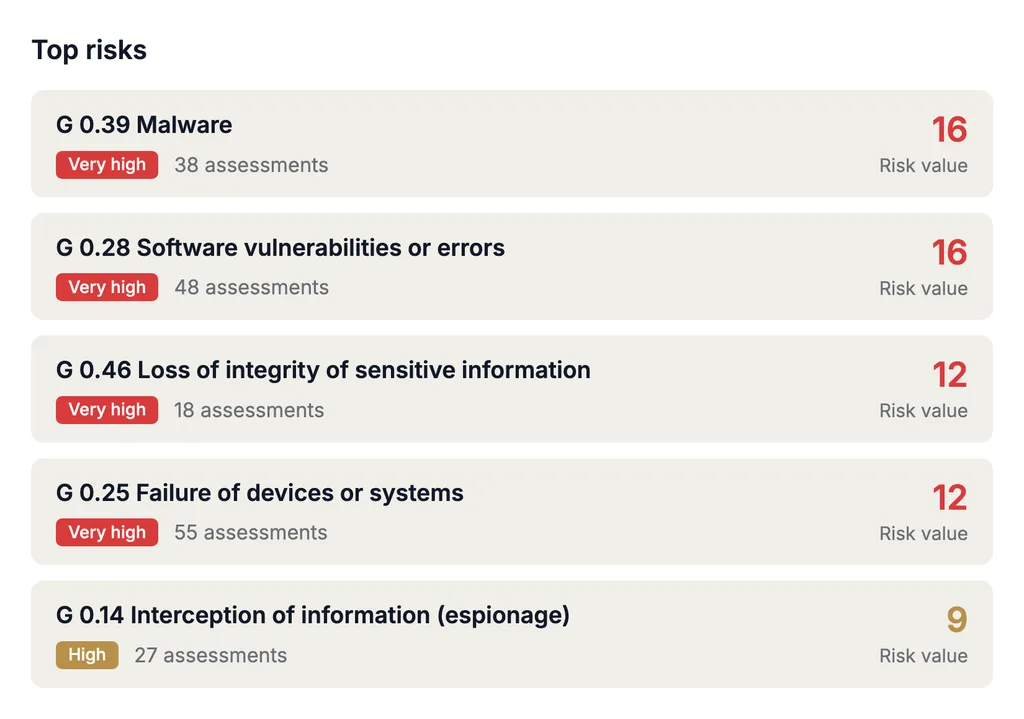
Risk analysis (Risikoanalyse): for target objects with high or very high protection needs — and for those that cannot be modelled adequately with the modules — you identify threats from the elementary threats (elementare Gefährdungen) of the Compendium or from your own catalogues and assess frequency of occurrence and impact in a configurable risk matrix. For every risk the treatment option is set, linked to requirements and measures, and the residual risk is tracked over time.
05 / 07 · Reporting & data analysis
Reference documents and reports for management and audit
Generate the reference documents (Referenzdokumente) A.1 to A.6 — structure analysis, protection needs determination, modelling, IT-Grundschutz Check, risk analysis and implementation plan (Realisierungsplan) — from your own data. Dashboards show management the state of the ISMS; distribution is handled by the Complaica Teams integration and the mail bot, and external BI and data analysis tools read the data over the REST API or data marts.
06 / 07 · Task management & collaboration
Implementation plan: measures and deadlines
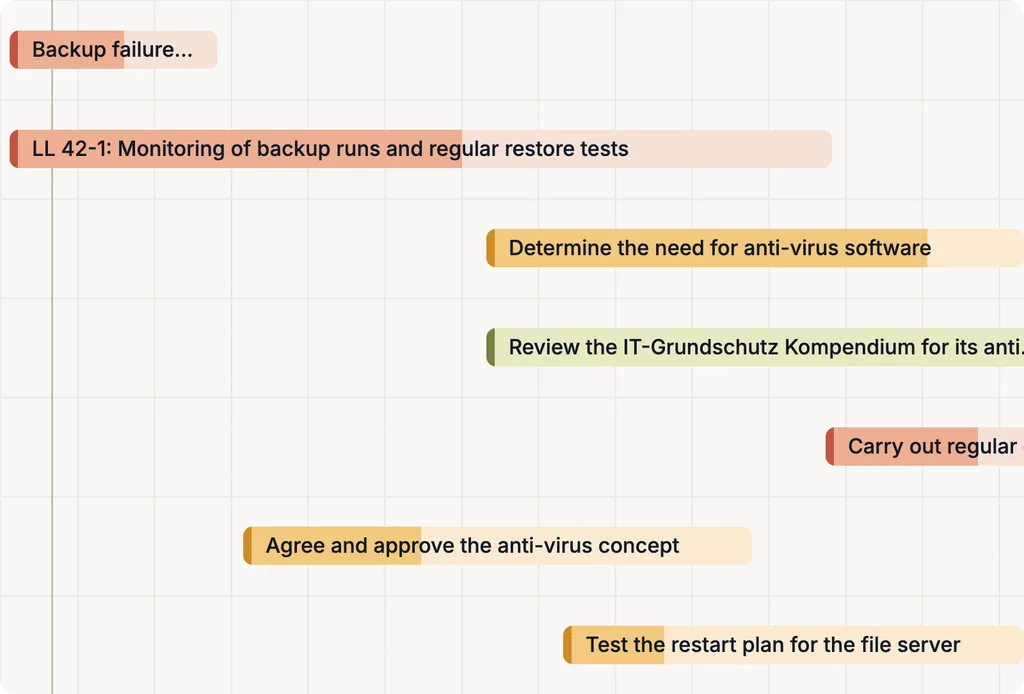
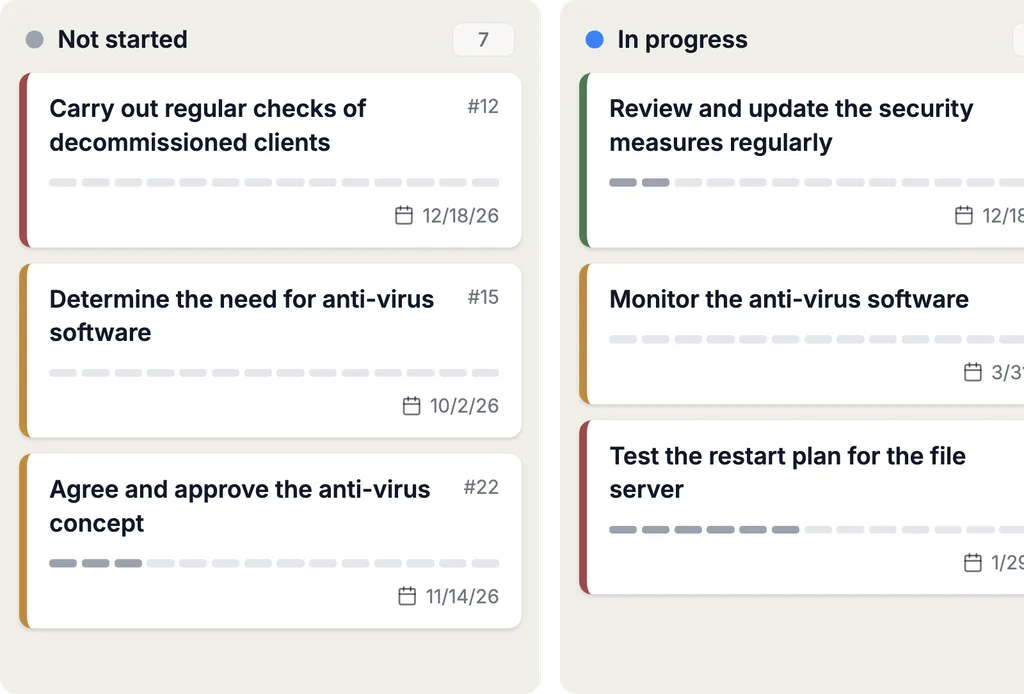
Open requirements and treated risks give rise to the implementation plan: measures and tasks carry owners, deadlines and status; every status change is recorded with author and date. Internal and external participants — auditors or service providers, say — work in the same system: access to individual target objects and documents is granted per object and by link.
07 / 07 · Integrations & automation
Complaica integrations
Over the REST API Complaica connects asset management and CMDB systems — Microsoft Azure, i-doit, GLPI, FNT Command and others — and keeps the structure analysis in step with reality. Jira, Microsoft Planner and others can be connected as task systems.
Application data is available through preset data marts, the REST API or MCP for external analysis and reporting systems.
IT-Grundschutz tool: every step of the methodology
As an IT-Grundschutz tool, Complaica supports every step of the IT-Grundschutz methodology according to BSI-Standard 200-2 — from the information domain to the audit. Every step works on the results of the previous one, in one connected data set.
- 01
Information domain
Informationsverbund
Define the organisation, sites and business processes the security concept applies to.
- 02
Structure analysis
Strukturanalyse
Record applications, IT systems, networks and rooms, group them and link them to the processes.
- 03
Protection needs determination
Schutzbedarfsfeststellung
Rate confidentiality, integrity and availability per target object; protection needs are inherited.
- 04
Modelling
Modellierung
Assign modules of the IT-Grundschutz Compendium to the target objects.
- 05
IT-Grundschutz Check
Target/actual comparison
Assess the implementation status of every requirement — with justification and evidence.
- 06
Risk analysis
BSI-Standard 200-3
Where protection needs are increased, identify threats, then assess and treat the risks.
- 07
Implementation planning
Realisierungsplanung
Consolidate and prioritise measures and implement them with owners and deadlines.
- 08
Audit
Maintenance and improvement
Reference documents A.1 to A.6 and evidence for internal audit and certification audit.
IT-Grundschutz Compendium and migration to Grundschutz++
The framework evolves, your ISMS stays: Complaica keeps the IT-Grundschutz Compendium current and carries Grundschutz++ as a catalogue — the migration takes place on the existing data set.
- Regular updates of the Compendium
The IT-Grundschutz Compendium is included as a catalogue with modules, requirements and elementary threats. New editions and corrections from the BSI are provided regularly as a catalogue update.
- Assessments are preserved
With an update, existing assessments, measures and evidence stay in place. What has changed is reassessed — not the whole information domain.
- Grundschutz++ as a catalogue
The BSI is developing IT-Grundschutz further into Grundschutz++: a process-oriented framework in a machine-readable format, whose user catalogue replaces the Compendium. Complaica already supports Grundschutz++.
- Migration without rebuilding
Information domain, target objects, protection needs, risks, measures and evidence stay in place during the migration; the requirements of Grundschutz++ are assessed on the same objects. During the transition both frameworks can be run in parallel.
- Time for an orderly transition
The BSI’s milestone plan (as of September 2026) names 1 January 2027 for the start of certifiability of Grundschutz++ and 30 November 2031 for the end of certifiability of IT-Grundschutz.
Why Complaica as IT-Grundschutz software?
Six reasons organisations build and run their ISMS according to IT-Grundschutz with Complaica.
Software plus expert consulting
ISMS software and consulting from one source: our compliance experts accompany setup, operation and audit preparation — as far as you need.
IT-Grundschutz ready to use — Compendium and BSI standards
The modules of the IT-Grundschutz Compendium with their requirements and elementary threats, the steps of the methodology according to BSI-Standard 200-2, the risk analysis according to BSI-Standard 200-3 and report templates for the reference documents are prepared. You do not start from zero.
One connected data set instead of Excel, PowerPoint and shared folders
Target objects, protection needs, modules, risks, measures and evidence stay connected in one data model — instead of being scattered across spreadsheets, presentations and shared folders and kept consistent by hand.
Compendium updates and Grundschutz++ included
Catalogue updates keep the Compendium current, and Grundschutz++ is assessed on the same data set — the migration is a transition, not a rebuild.
From the first audit to recertification
One data set for initial certification, surveillance audits and recertification: the state of the ISMS stays current between audits, nothing is rebuilt.
IT-Grundschutz with AI support
With the optional AI integration (MCP), Complaica answers questions on IT-Grundschutz, explains modules and requirements, helps with measures and tasks and finds answers in your own policies and documents. It supports the work in the ISMS — assessment and decision stay with you.
- 01Answer questions on the IT-Grundschutz methodology and the Compendium
- 02Explain modules and requirements — what is required and what counts as evidence
- 03Suggest, formulate and assign measures and tasks
- 04Analyse your policies, procedures and documents and answer questions about them
- 05Explain how to use Complaica — which function for what
Customer voices on the ISMS with Complaica
“The optimised compliance process”
One of the features we like best about Complaica is the optimised compliance process. The user interface has a clear, structured design that offers more usability and encourages a higher working speed. This not only gives new users a steep learning curve, it also lets experienced users minimise their effort. In every phase of the security management lifecycle, recurring tasks such as scoping, structure analysis, modelling and even the tracking of risks and measures are supported by a wealth of functionality. On top of that the platform’s performance is great — it is stable and excellent in terms of speed.
More …Less
One of the features we like best about Complaica is the optimised compliance process. The user interface has a clear, structured design that offers more usability and encourages a higher working speed. This not only gives new users a steep learning curve, it also lets experienced users minimise their effort.
In every phase of the security management lifecycle, recurring tasks such as scoping, structure analysis, modelling and even the tracking of risks and measures are supported by a wealth of functionality.
On top of that the platform’s performance is great — it is stable and excellent in terms of speed.
“We can do everything we need in one tool”
Complaica is extremely user-friendly and customising it is child’s play. We can take care of ISO compliance and data protection with it — we can do everything we need in one tool. For us, Complaica is better than the alternatives on the market and cheaper at the same time.
More …Less
Complaica is extremely user-friendly and customising it is child’s play. We can take care of ISO compliance and data protection with it — we can do everything we need in one tool.
For us, Complaica is better than the alternatives on the market and cheaper at the same time.
“The guided approach played a decisive role for us”
We were new to compliance and to implementing ISO 27001, and had to go through the complicated certification process. Given the regulatory complexity, we wanted to find the best way for us to get started. Our project manager (aka security officer) had never worked with such compliance standards and rules before. So we decided on support from a third party — Complaica, to be precise. The guided approach played a decisive role for us. Complaica had all the detailed explanations for the compliance check and the risk analysis, including practical suggestions.
More …Less
We were new to compliance and to implementing ISO 27001, and had to go through the complicated certification process.
Given the regulatory complexity, we wanted to find the best way for us to get started. Our project manager (aka security officer) had never worked with such compliance standards and rules before.
So we decided on support from a third party — Complaica, to be precise. The guided approach played a decisive role for us. Complaica had all the detailed explanations for the compliance check and the risk analysis, including practical suggestions.
IT-Grundschutz consulting
Information security as a service: consulting along the IT-Grundschutz methodology — from gap analysis to audit preparation and the migration to Grundschutz++, to the extent you need.
- Gap analysis and preparation
Comparison of your current state with the requirements of the IT-Grundschutz Compendium. Result: a prioritised list of gaps and an implementation plan.
- Setup and introduction of the ISMS
Security organisation, policy, scope and roles according to BSI-Standard 200-1 and 200-2 — with the approach that suits you: Basic, Standard or Core Protection.
- Structure analysis, protection needs and modelling
The information domain is set up in Complaica: target objects recorded and grouped, protection needs determined, modules assigned.
- Risk analysis and measure planning
Risk analysis according to BSI-Standard 200-3 for target objects with increased protection needs, choose treatment options and derive the implementation plan.
- Audits and audit preparation
Internal audits, management review and preparation for the certification audit — with the reference documents the auditor wants to see.
- Migration to Grundschutz++
Planning and accompanying the transition from the IT-Grundschutz Compendium to Grundschutz++, on your existing data set.
- External information security officer
A contact for your ISMS, for a time or permanently — for organisations without a role of their own for it.
IT-Grundschutz and further standards
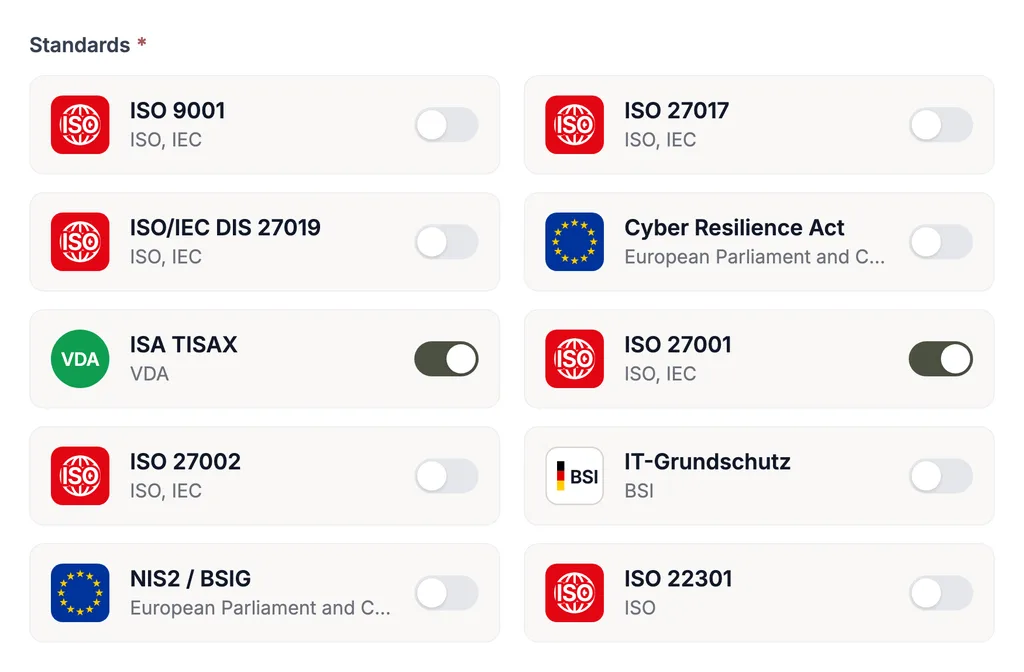
IT-Grundschutz is rarely the only framework that applies to an organisation. In Complaica the requirements of further standards use the same target objects, risks, measures and evidence: what is documented for IT-Grundschutz also counts for an ISMS according to ISO 27001, for NIS2, DORA, TISAX or data protection management under the GDPR. No duplicate maintenance.
Every standard ships with its requirement catalogue; your own catalogues can be added at any time. All areas are shown by the GRC platform Complaica.
Frequently asked questions about IT-Grundschutz software
What is BSI IT-Grundschutz?
IT-Grundschutz is the methodology of the German Federal Office for Information Security (BSI) for setting up and running an information security management system (ISMS). It consists of the BSI standards — 200-1 for the management system, 200-2 for the methodology, 200-3 for risk analysis — and the IT-Grundschutz Compendium, whose modules describe, in ten layers, the requirements and the elementary threats for each topic.
What is IT-Grundschutz software?
IT-Grundschutz software is ISMS software that maps the methodology of the BSI in one data model: information domain, target objects, protection needs, modules, requirements, risks, measures and evidence are linked to each other. Instead of keeping spreadsheets and documents consistent by hand, you maintain every object once, and reports such as the reference documents are generated from the data.
Which tool supports BSI IT-Grundschutz?
A suitable choice is an IT-Grundschutz tool that brings the IT-Grundschutz Compendium along as a catalogue and maps every step of the methodology according to BSI-Standard 200-2. Complaica is such a tool: structure analysis, protection needs determination, modelling, IT-Grundschutz Check, risk analysis and implementation planning work on one data set, as SaaS or On-Premises.
Which steps of the IT-Grundschutz methodology does Complaica support?
All steps according to BSI-Standard 200-2: defining the information domain (Informationsverbund), the structure analysis (Strukturanalyse), the protection needs determination (Schutzbedarfsfeststellung), modelling (Modellierung) with the modules (Bausteine) of the Compendium, the IT-Grundschutz Check, the risk analysis (Risikoanalyse) according to BSI-Standard 200-3, implementation planning (Realisierungsplanung), and maintenance, audit and continual improvement. Every step works on the results of the previous one, in one data set.
Does Complaica support BSI-Standard 200-1, 200-2 and 200-3?
Yes. Complaica implements the BSI standards 200-1 (Information Security Management Systems), 200-2 (IT-Grundschutz Methodology) and 200-3 (Risk Analysis based on IT-Grundschutz). The steps of the methodology and the risk analysis are mapped as workflows in the software, and the IT-Grundschutz Compendium is included as a catalogue.
Does Complaica support Basic, Standard and Core Protection?
Yes. BSI-Standard 200-2 knows three approaches: Basic Protection is the entry into an ISMS, Core Protection first looks at a small, particularly important part of the information domain, and Standard Protection implements a complete security process. In Complaica, basic requirements, standard requirements and requirements for increased protection needs can be evaluated separately, so you can begin with one approach and extend later.
How does structure analysis work in Complaica?
Target objects — business processes, applications, IT systems, networks, rooms — are recorded or imported from asset management, CMDBs and Microsoft Azure, combined into groups and linked along their dependencies. Dependency graph and dependency matrix show the structure of the information domain; the structure analysis is available as reference document A.1.
How does protection needs determination work in Complaica?
Protection needs are determined per target object for confidentiality, integrity and availability — normal, high or very high. Along the dependencies they are inherited by the maximum principle; the origin of every rating can be displayed.
How do modelling and the IT-Grundschutz Check work in Complaica?
In modelling, the matching modules of the IT-Grundschutz Compendium are assigned to the target objects. In the IT-Grundschutz Check, the target/actual comparison, you assess the implementation status of every requirement, justify it and store evidence. The status cumulates from the individual target object up to the information domain, and open requirements go into the implementation plan.
Does Complaica support risk analysis according to BSI-Standard 200-3?
Yes. For target objects with high or very high protection needs, and for those that cannot be modelled adequately with the modules, threats are identified — from the elementary threats of the Compendium or from your own catalogues — and assessed in a configurable risk matrix. For every risk, the treatment option and measures are set; the residual risk can be tracked over time.
Does Complaica generate the reference documents A.1 to A.6?
Yes. Structure analysis (A.1), protection needs determination (A.2), modelling (A.3), result of the IT-Grundschutz Check (A.4), risk analysis (A.5) and implementation plan (A.6) are generated as reports from the current data set — at the initial audit and before every surveillance audit, without rewriting the documents.
Does Complaica support the IT-Grundschutz Compendium?
Yes. The IT-Grundschutz Compendium is included as a catalogue with its modules, requirements and elementary threats. When the BSI publishes a new edition or corrections, the catalogue is updated and provided as an update; existing assessments, measures and evidence are preserved.
What is Grundschutz++?
Grundschutz++ is the BSI’s redevelopment of Grundschutz: a fully process-oriented framework whose requirements are available in a machine-readable format and can therefore be evaluated by tools. The Grundschutz++ user catalogue replaces the IT-Grundschutz Compendium.
Does Complaica support Grundschutz++?
Yes. Complaica is one of the first tools with support for BSI Grundschutz++. The requirements of Grundschutz++ are carried as a catalogue and assessed on the same data set as IT-Grundschutz.
How does the migration to Grundschutz++ work?
The migration takes place on the existing data set: information domain, target objects, protection needs, risks, measures and evidence stay in place, and the requirements of Grundschutz++ are assessed on the same objects. During the transition both frameworks can be run in parallel. On request, our consultants accompany the migration.
How long can IT-Grundschutz still be certified?
According to the BSI’s milestone plan (as of September 2026), certification applications for ISO 27001 on the basis of Grundschutz++ can be submitted from 1 January 2027; the certifiability of IT-Grundschutz ends on 30 November 2031. The BSI adjusts the plan continuously — the version on the BSI’s website is the authoritative one.
What is the difference between IT-Grundschutz and ISO 27001?
ISO/IEC 27001 describes what an ISMS must achieve and leaves the design to the organisation. IT-Grundschutz adds a concrete methodology to that and, with the modules of the Compendium, detailed requirements. The two can be combined: Standard Protection is compatible with ISO 27001 certification, and the certificate is then called “ISO 27001 on the basis of IT-Grundschutz”. In Complaica both run on the same data set.
Can an existing ISMS be taken over from Excel or other systems?
Yes. Complaica imports and exports data from and to Excel, over the REST API and from other ISMS tools; migrating your data is free and accompanied by our specialists. So you evaluate the tool on your own data set rather than on demo data.
Can Complaica manage several standards at once?
Yes. ISO 27001, NIS2, TISAX, GDPR, ISO 22301 and further standards are assessed on the same model and use the same target objects, risks, measures and evidence. What is documented for IT-Grundschutz counts for the other standards too.
Is Complaica available as SaaS and On-Premises?
Yes, both. The SaaS variant is hosted in Germany; On-Premises you run Complaica in your own infrastructure. The licence costs the same either way.
How does Complaica support the IT-Grundschutz audit and certification?
Evidence sits on the object it proves, and the reference documents are generated from the current data set. Dashboards show the state before the audit, and external auditors can be given targeted access. Because the same data set keeps running, surveillance audits and recertification are prepared out of ongoing operation. The certification itself is performed by the BSI on the basis of the audit by a certified auditor.
Start IT-Grundschutz with Complaica
Test the IT-Grundschutz software, request a demo or talk about your existing ISMS and the migration to Grundschutz++ — write to us.
Thank you.
We will get back to you within one business day.
Not sent.
That did not work. Please check the fields or email us directly.