ISO 13485 software
for medical devices
Run your medical device quality management system to ISO 13485:2016 on one set of data: products and medical device files, processes, risk management, suppliers, complaints, CAPA and internal audits — from set-up to recertification, with consulting as you need it.
- 01ISO 13485:2016 requirements catalogue — clauses 4 to 8, each requirement assessed on its own
- 02Products, medical device files and risk management as linked objects
- 03Complaints, corrective and preventive actions with deadlines and status
- 04Internal audits and management review from one set of data
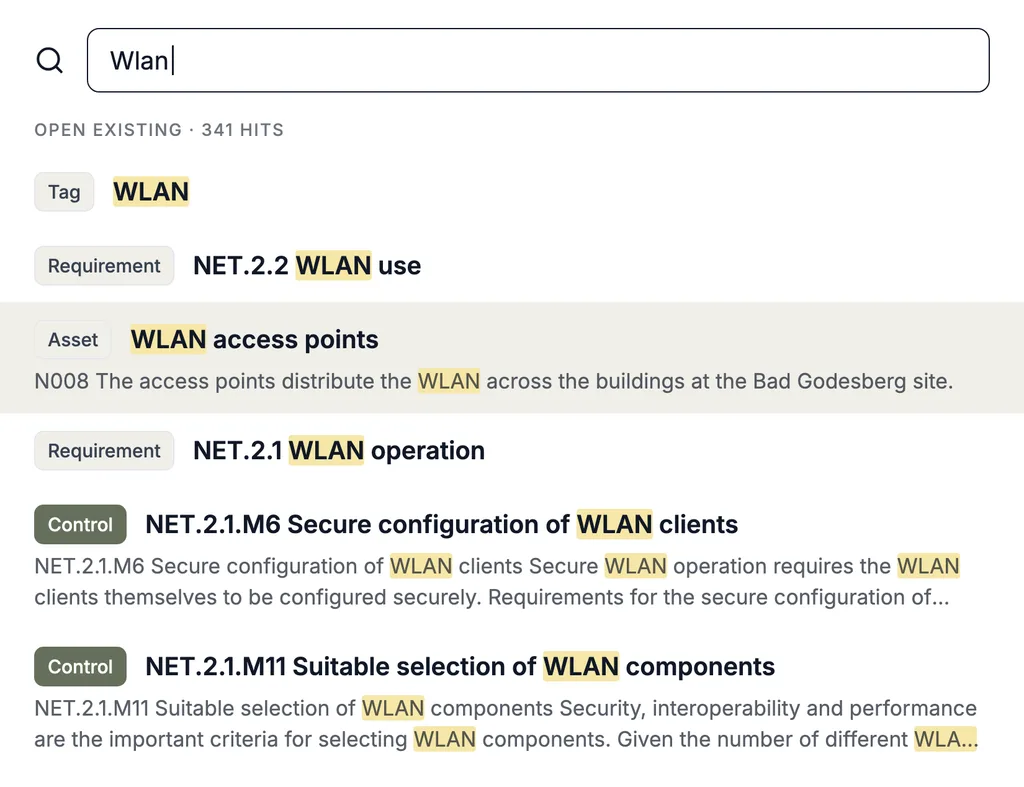
- 05One integrated management system with ISO 9001, ISO 27001, GDPR and other standards
Build and run a medical device QMS to ISO 13485
The functions with which Complaica ISO 13485 software covers the quality management system for medical devices — from the requirements catalogue through products, risks and suppliers to complaints, CAPA, the internal audit and the management review.
- 01ISO 13485:2016 requirements catalogue with every clause from 4 to 8 — each requirement with status, owners, documents and notes; requirements that do not apply with their justification
- 02Products and product families as objects: medical device file, design and development records and risk management assigned to the product
- 03Processes with owners, inputs, outputs and interactions, outsourced processes included
- 04Assess risks per product and per process in configurable matrices and link them to actions
- 05Design and development under clause 7.3: planning, reviews, verification, validation, transfer and changes as tasks with owners and deadlines
- 06Control of documents and records — every change traceable with author and date
- 07Record suppliers and outsourced processes, evaluate them by risk and monitor them
- 08Complaints, incidents and reports to regulatory authorities as records with deadlines and status
- 09Corrective and preventive actions (CAPA) with root-cause analysis, deadlines and effectiveness check
- 10Plan and carry out internal audits, turn findings into actions
- 11Reports and dashboards for the management review — from the data, not from slides
- 12AI integration (MCP) for questions on ISO 13485, on requirements and evidence, and on using the product
ISO 13485 requirements — clauses 4 to 8
ISO 13485:2016 still follows the clause structure of ISO 9001:2008, not the harmonized structure of ISO 9001 and ISO 27001. The requirements are in clauses 4 to 8; for each, here is what Complaica keeps for it.
Scope and terms
The scope with the rules for requirements that do not apply, normative references and the standard's own terms — medical device, complaint, life cycle, risk and more. These clauses hold no requirements yet.
In Complaica: the catalogue with an explanation of every requirement and the terms it rests on.
Quality management system
Processes with a risk-based approach, control of outsourced processes, validation of the software used in the QMS, the quality manual, the medical device file and control of documents and records — kept for at least the lifetime of the device, and no less than two years.
In Complaica: processes and products as linked objects, documents on the object with the author and date of every change.
Management responsibility
Top management sets the quality policy and objectives, defines responsibility and authority, appoints a management representative and reviews the QMS at planned intervals — with inputs such as feedback, complaints, reports to regulatory authorities, audits and CAPA.
In Complaica: quality policy and objectives on the object, roles per process and product, reports as input to the management review.
Resource management
Competent personnel and training whose effectiveness is evaluated, infrastructure with its maintenance, the work environment and contamination control.
In Complaica: training and evidence of competence, equipment and facilities as objects with maintenance tasks.
Product realization
Planning with risk management, customer-related processes, design and development from planning to transfer with its design and development file, purchasing with supplier evaluation, production with process validation, identification and traceability, and control of monitoring and measuring equipment.
In Complaica: development steps as tasks on the product, risks per product, supplier evaluation; suppliers, processes and documents linked per product.
Measurement, analysis and improvement
Feedback, complaint handling, reporting to regulatory authorities, internal audit, control of nonconforming product including after delivery, analysis of data, and corrective and preventive action.
In Complaica: complaints, nonconformities and CAPA as records with their own workflow, the audit programme and findings, dashboards for analysis.
ISO 13485, MDR, IVDR and the FDA QMSR
ISO 13485 is a voluntary standard — but the regulation of the major markets rests on it. A QMS to ISO 13485 covers much of the QMS requirements of the MDR, the IVDR and the FDA; what goes beyond it is in the regulations themselves.
- EU: MDR and IVDR
Manufacturers of medical devices and in vitro diagnostic devices must establish a QMS (Article 10 of Regulations (EU) 2017/745 and 2017/746). EN ISO 13485:2016 with amendment A11:2021 is harmonised under both; applying it gives a presumption of conformity with the requirements its Annexes ZA and ZB name.
- USA: FDA QMSR
Since 2 February 2026 the Quality Management System Regulation (21 CFR Part 820) applies in the USA. It incorporates ISO 13485:2016 by reference, together with the terms in clause 3 of ISO 9000:2015 and requirements of the FDA's own.
- MDSAP
Under the Medical Device Single Audit Program, a recognised auditing organisation audits the QMS once against ISO 13485 and the additional requirements of the authorities of Australia, Brazil, Canada, Japan and the USA.
- The 2016 edition stays
ISO 13485:2016 is the third edition; ISO confirmed it in its systematic review in 2025. The new ISO 9001:2026 changes nothing in ISO 13485 — the two standards stand apart.
- The catalogue in Complaica
Complaica updates its catalogues with new editions of a standard; existing assessments and evidence are kept, and the differences between editions become visible.
Information as of 8 November 2026
From folders and Excel to a central medical device QMS
A medical device QMS can be run in documents and spreadsheets — until device files, complaints, CAPA and audits start referring to each other and an auditor wants to see the chain. Four points where Complaica organises the work differently.
| Word and Excel | Complaica | |
|---|---|---|
| Medical device file | One folder per product, links to files on shared drives. | The product is an object; specifications, design and development records, risk management and approvals hang on it — a change shows wherever it has an effect. |
| Complaints and CAPA | A complaints list, actions in a second one, reconciled by hand. | Complaint, nonconformity and action are linked records with owners, deadlines, status and an effectiveness check. |
| Control of documents | The version in the file name, approval by e-mail. | Every change is recorded with author and date; documents sit on the requirement and the product they prove. |
| Several rule sets | ISO 13485, MDR requirements and ISO 9001 in separate spreadsheets. | The same processes, risks and evidence for ISO 13485, your own catalogues, ISO 9001 or ISO 27001 — where the content fits. |
Complaica modules for the QMS
Seven modules, one connected data set: organisation, products and processes, requirements catalogue, risk management, reports, CAPA and integrations work on the same objects.
01 / 07 · Organisation management
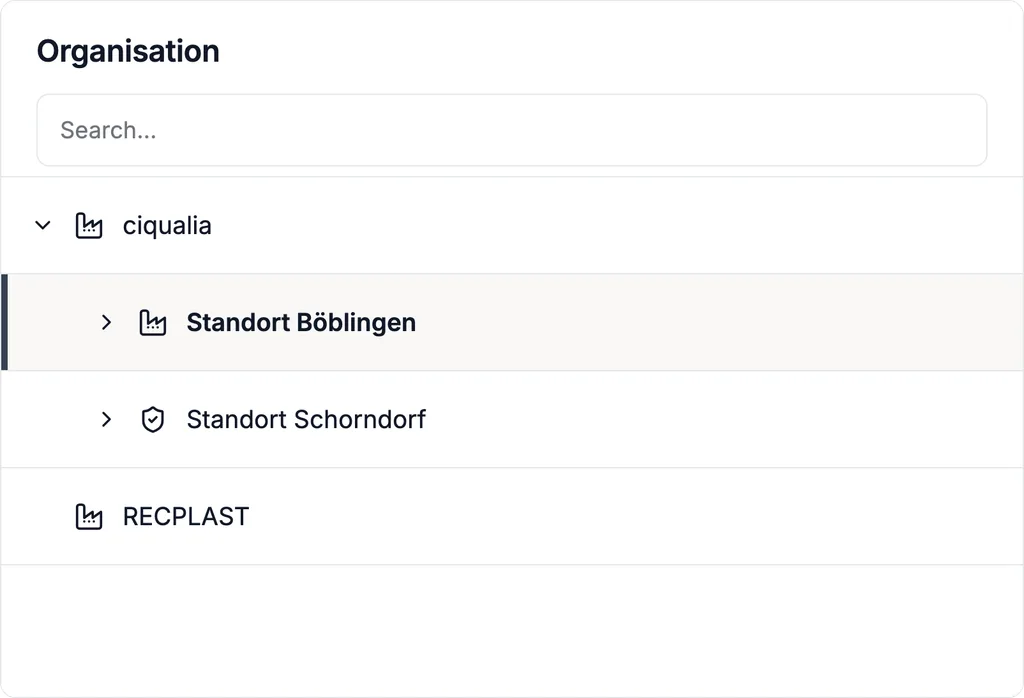
Organisation, sites and scope
Map your organisation as a tree — companies, sites, departments, units — and set what belongs to the scope of the QMS. Responsibilities are assigned per unit and per object; access rights follow the same structure.
02 / 07 · Processes and dependencies
Products, processes and the medical device file
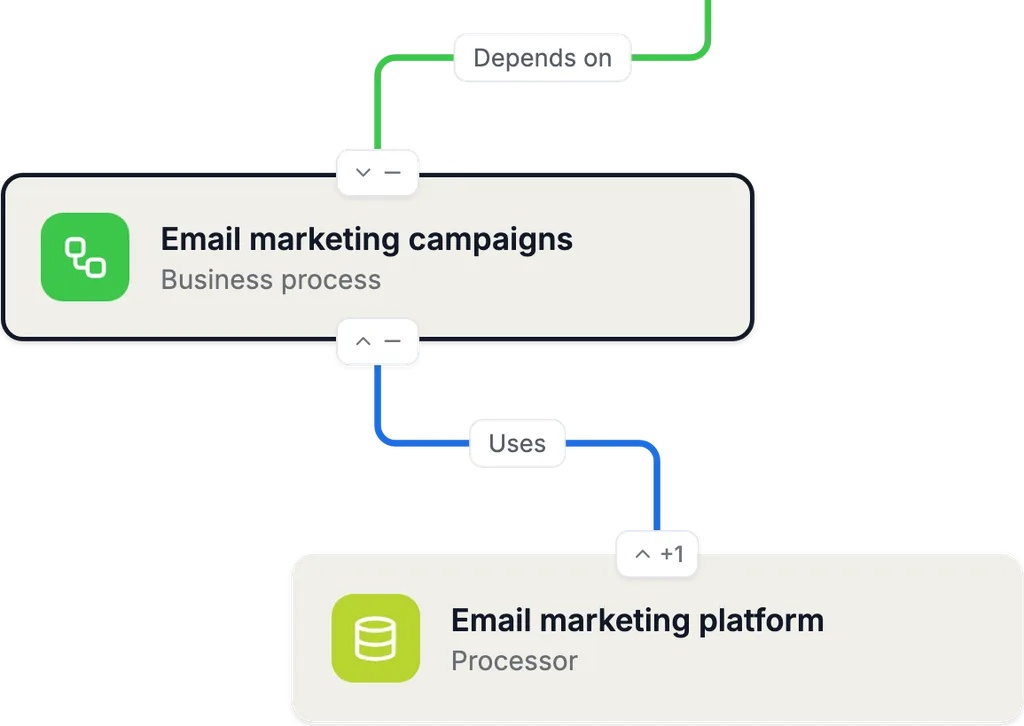
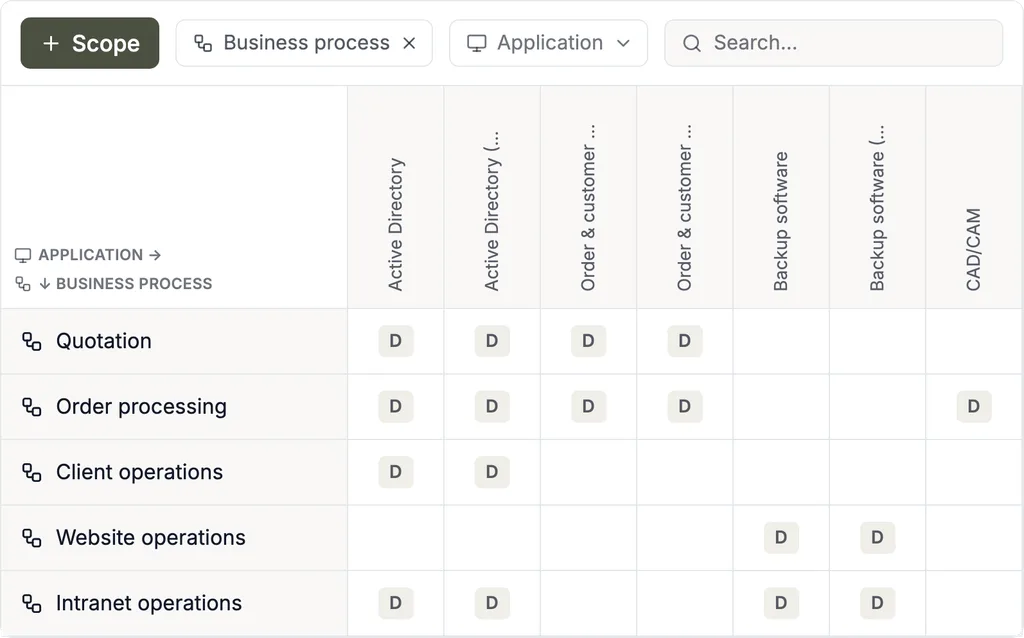
Record products and product families as objects and link them to the processes, suppliers, sites and documents they depend on — specifications, design and development records, risk management, approvals. That gives each product the context ISO 13485 asks for in the medical device file (clause 4.2.3).
Dependency graphs and matrices show which product and which process are affected when a supplier, a component, a system or a rule changes.
03 / 07 · Compliance management
ISO 13485:2016 requirements catalogue
Assess every requirement of clauses 4 to 8 — implemented, partly implemented, open, or not applicable with a justification — with owners, documents, tasks and notes. The level of fulfilment rolls up to subclause, clause and overall status.
Your own rules — the quality manual, MDR and IVDR requirements, customer requirements — are assessed as catalogues of your own on the same model. What is documented for ISO 9001 or ISO 27001 can be used for ISO 13485 where the content fits.
04 / 07 · Risk management
Risk management across the life cycle
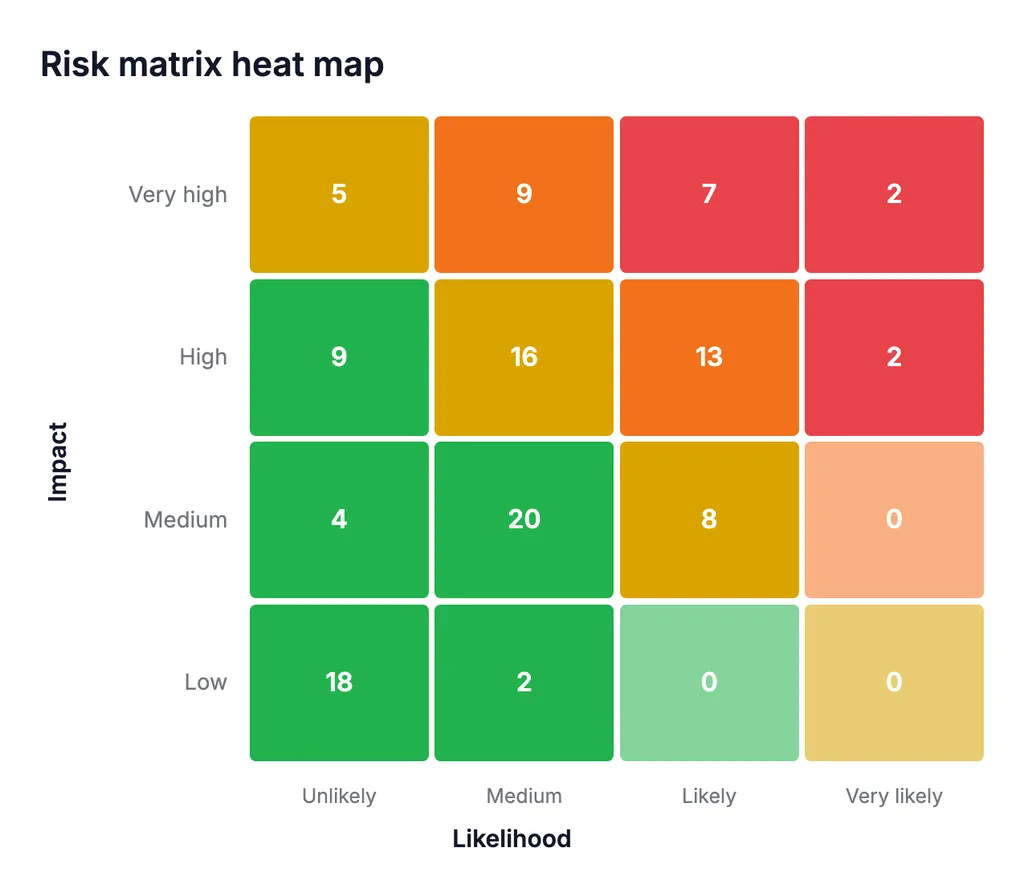
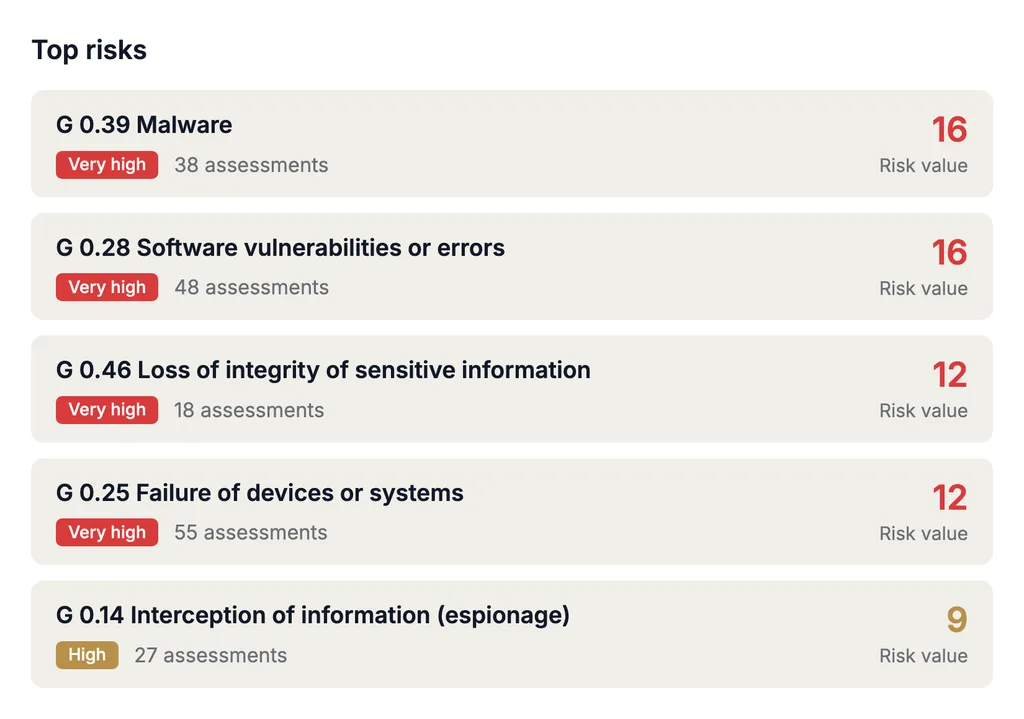
ISO 13485 asks for a risk-based approach to the processes of the QMS and documented risk management in product realization; ISO 14971 describes the method. Assess risks per product and per process in a configurable matrix, link them to actions and track the residual risk over time.
05 / 07 · Reporting & data analysis
Reports for the management review and the audit
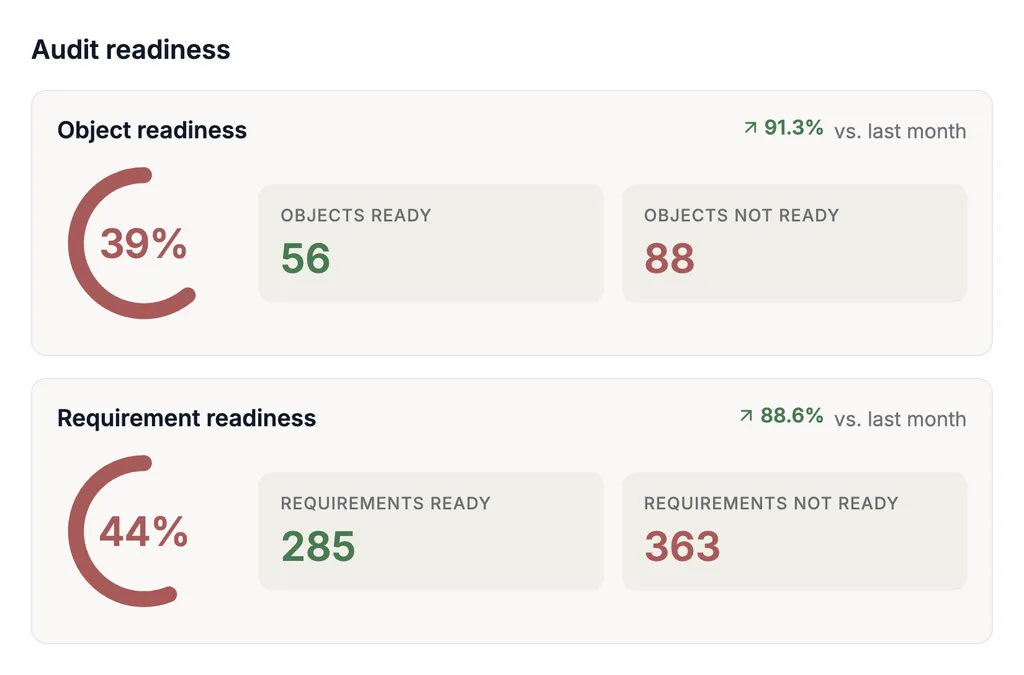
Generate reports on the level of fulfilment per clause, on complaints, CAPA, audit findings and quality objectives from your own data — as a report template or a custom report. Dashboards show management where things stand before the review; external BI tools read the data through the REST API or data marts.
06 / 07 · Task management & collaboration
Complaints, CAPA and deadlines
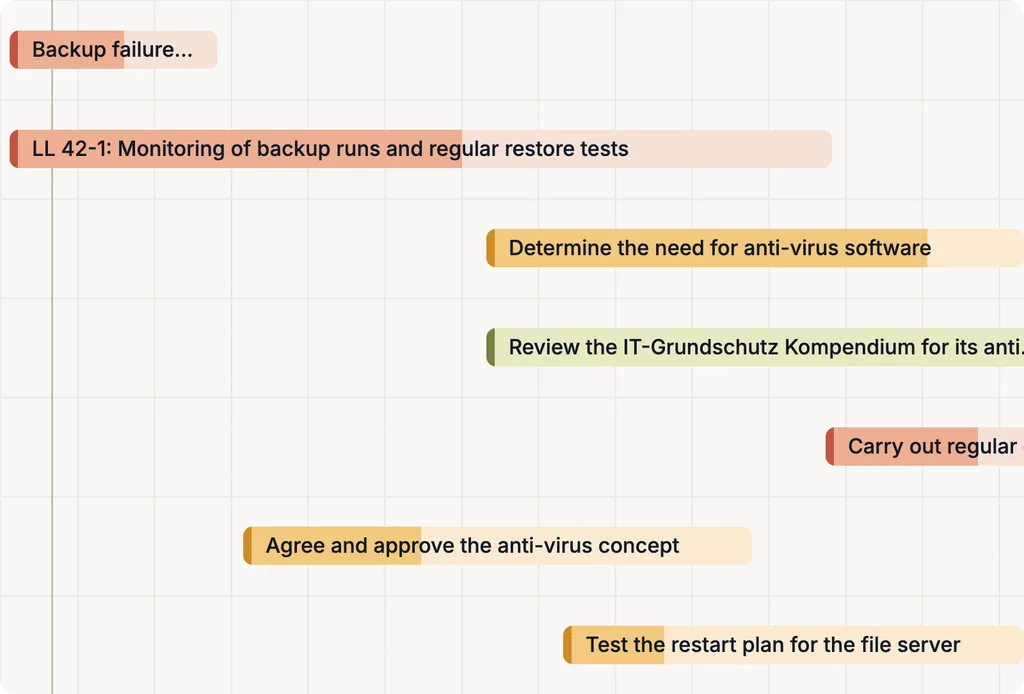
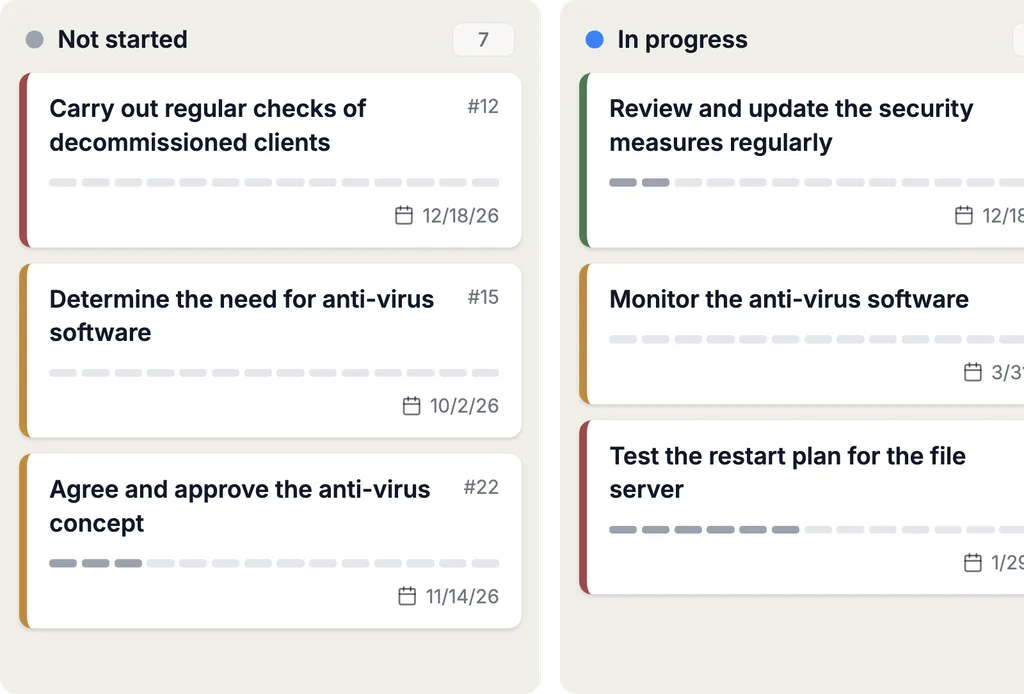
Complaints, incidents, nonconformities and corrective and preventive actions are kept as records with owners, deadlines and status; every status change is recorded with author and date. Suppliers and auditors work in the same system: access is granted per object and by link. How audits are planned and run is shown on the audit management page.
07 / 07 · Integrations & automation
Complaica integrations
Through its REST API, Complaica connects ERP, asset management and CMDB systems — SAP, Microsoft Azure, i-doit and others — and keeps the processes and resources in the QMS in step with reality. Jira, Microsoft Planner and others can be connected as the task system.
Application data is available to external analysis and reporting systems through preconfigured data marts, the REST API or MCP.
Five steps to ISO 13485 certification
From the scope to recertification — and what Complaica takes on at each step.
- 01
DefineRole, markets, scope
Determine the organisation's role — manufacturer, supplier, distributor —, the target markets and their regulatory requirements, the scope and the requirements that do not apply. In Complaica this becomes products, processes and catalogues.
- 02
Build
Quality manual, documented procedures, medical device files, risk management, supplier evaluation and the validation of the software used in the QMS. The gap analysis against the requirements catalogue shows what is still missing.
- 03
CheckInternal audit and management review
Internal audit to the audit programme, findings turned into corrective actions, management review with the inputs of clause 5.6.2.
- 04
CertifyStage 1 and stage 2
An accredited certification body reviews the documentation and the implementation. For CE marking, depending on the class, a notified body assesses the QMS under the MDR or IVDR — often in the same audit.
- 05
MaintainSurveillance and recertification
Annual surveillance audits, recertification after three years; notified bodies also audit unannounced. Complaints, CAPA and changes carry on in Complaica.
Why a QMS to ISO 13485?
What a QMS to ISO 13485 brings manufacturers and suppliers of medical devices.
- 01Market access in the EU — EN ISO 13485 is harmonised under the MDR and IVDR
- 02Market access in the USA — the FDA QMSR has incorporated ISO 13485:2016 since February 2026
- 03One audit for several markets through MDSAP: Australia, Brazil, Canada, Japan, USA
- 04For suppliers: many manufacturers require ISO 13485 for critical parts and services
- 05Patient safety through risk management across the whole life cycle of the device
- 06Traceability that holds when an incident or a recall happens
- 07A foundation for an integrated management system with ISO 9001, information security and data protection
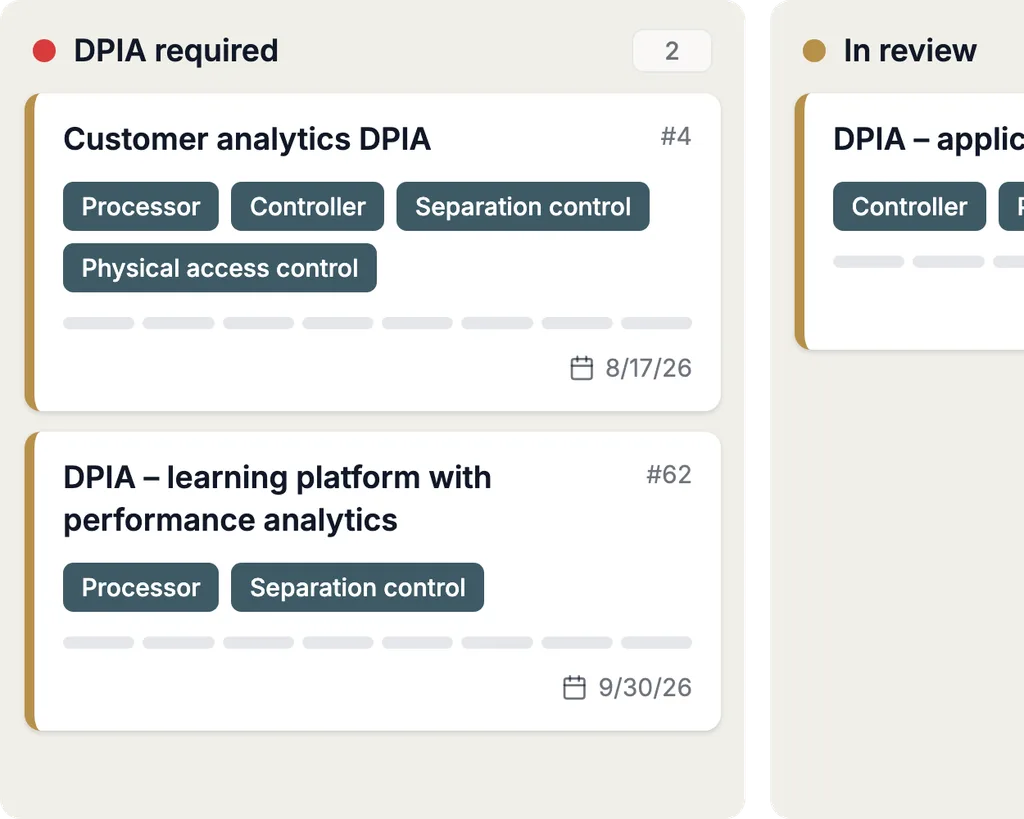
Why Complaica as ISO 13485 software?
Six reasons manufacturers and suppliers run their medical device QMS with Complaica.
Products, not folders
A product is an object with design, risks, suppliers, documents and approvals — not a folder that is put together again after every change.
Granular requirements
Each ISO 13485 requirement is assessed on its own and linked to documents, tasks and owners — visible per clause, per process and per product.
From complaint to CAPA
Feedback, complaint, report, nonconformity, corrective and preventive action: one path on one set of data, with an effectiveness check and a report for the management review.
Consulting from one source
Our consultants support the set-up, the internal audit and certification, and walk you through every function of the product.
Traceable for auditors and authorities
Every change is recorded with author and date; evidence sits on the requirement and the product it proves.
Streamline compliance tasks with AI assistance
With the optional AI integration (MCP), Complaica answers questions on ISO 13485, explains requirements, helps with complaints, CAPA and tasks, and finds answers in your own procedures and documents. It supports the work on the QMS — assessment and decisions stay with you.
- 01Answer questions on ISO 13485 and how it relates to the MDR, IVDR and FDA QMSR
- 02Explain requirements — what is asked for and what counts as evidence
- 03Suggest, word and assign corrective and preventive actions
- 04Evaluate your procedures, device files and documents and answer questions on them
- 05Explain how to use Complaica — which function is for what
What customers say about Complaica
“We can do everything we need in one tool”
Complaica is extremely user-friendly and customising it is child’s play. We can take care of ISO compliance and data protection with it — we can do everything we need in one tool. For us, Complaica is better than the alternatives on the market and cheaper at the same time.
More …Less
Complaica is extremely user-friendly and customising it is child’s play. We can take care of ISO compliance and data protection with it — we can do everything we need in one tool.
For us, Complaica is better than the alternatives on the market and cheaper at the same time.
“The optimised compliance process”
One of the features we like best about Complaica is the optimised compliance process. The user interface has a clear, structured design that offers more usability and encourages a higher working speed. This not only gives new users a steep learning curve, it also lets experienced users minimise their effort. In every phase of the security management lifecycle, recurring tasks such as scoping, structure analysis, modelling and even the tracking of risks and measures are supported by a wealth of functionality. On top of that the platform’s performance is great — it is stable and excellent in terms of speed.
More …Less
One of the features we like best about Complaica is the optimised compliance process. The user interface has a clear, structured design that offers more usability and encourages a higher working speed. This not only gives new users a steep learning curve, it also lets experienced users minimise their effort.
In every phase of the security management lifecycle, recurring tasks such as scoping, structure analysis, modelling and even the tracking of risks and measures are supported by a wealth of functionality.
On top of that the platform’s performance is great — it is stable and excellent in terms of speed.
“The guided approach played a decisive role for us”
We were new to compliance and to implementing ISO 27001, and had to go through the complicated certification process. Given the regulatory complexity, we wanted to find the best way for us to get started. Our project manager (aka security officer) had never worked with such compliance standards and rules before. So we decided on support from a third party — Complaica, to be precise. The guided approach played a decisive role for us. Complaica had all the detailed explanations for the compliance check and the risk analysis, including practical suggestions.
More …Less
We were new to compliance and to implementing ISO 27001, and had to go through the complicated certification process.
Given the regulatory complexity, we wanted to find the best way for us to get started. Our project manager (aka security officer) had never worked with such compliance standards and rules before.
So we decided on support from a third party — Complaica, to be precise. The guided approach played a decisive role for us. Complaica had all the detailed explanations for the compliance check and the risk analysis, including practical suggestions.
ISO 13485 consulting
Consulting along the medical device QMS — from the scope to recertification, as much as you need.
- Gap analysis
Your current state against the requirements of ISO 13485:2016. Result: the level of fulfilment per clause, a prioritised list of gaps and an implementation plan.
- From ISO 9001 to ISO 13485
For organisations with a QMS to ISO 9001: assess the additional requirements — medical device file, risk management, validation, complaints and reporting — and extend the existing system.
- Setting up the QMS
Products, processes, roles and documented procedures are set up in Complaica. You get a working QMS.
- Internal audits
Set up the audit programme, carry out or accompany internal audits, turn findings into corrective actions.
- Preparing for certification
Prepare stage 1 and stage 2, provide evidence the way auditors and notified bodies want to see it, support the management review.
- Integrated management system
Connect ISO 13485 with ISO 9001, ISO 27001 or data protection on one set of data — shared processes, risks and audits.
SaaS or on-premises
Complaica runs where your organisation needs it — the licence costs the same either way.
- SaaS, hosted in Germany
The SaaS edition is operated in Germany; you work in the browser, with no infrastructure of your own.
- On-premises in your infrastructure
You run Complaica in your own environment — for organisations whose data may not leave the house.
- Bring your existing data
Import and export from and to Excel and through the REST API; our specialists support the move of your data free of charge.
ISO 13485 in an integrated management system
ISO 13485 is closely related to ISO 9001 but still follows the clause structure of ISO 9001:2008. In Complaica both standards use the same processes, risks, actions and evidence: what is documented for the QMS can be used, where the content fits, for ISO 9001, an ISMS to ISO 27001, for NIS2 or data protection management under the GDPR.
Every standard ships with its requirements catalogue; your own catalogues can be added at any time.
Frequently asked questions about ISO 13485 software
What is ISO 13485?
ISO 13485 is the international standard for the quality management systems of organisations that design, manufacture, install, service or distribute medical devices, and of their suppliers. It requires regulatory and customer requirements to be met consistently and puts particular weight on risk management, validation, traceability and documented procedures. The current edition is the third, ISO 13485:2016.
How does ISO 13485 differ from ISO 9001?
ISO 13485 builds on the structure of ISO 9001:2008, not on the harmonized structure of today's ISO 9001. It aims at the effectiveness of the QMS and at meeting regulatory requirements, and asks for more documented procedures, the medical device file, risk management in product realization, validation of processes and software, complaint handling and reporting to authorities. An ISO 9001 certificate does not replace an ISO 13485 certificate.
Is ISO 13485 mandatory?
The standard itself is voluntary. The MDR and IVDR do require manufacturers to have a QMS, and the harmonised EN ISO 13485 is the usual way to show it; in the USA, ISO 13485:2016 has been part of the regulation through the FDA QMSR since 2 February 2026. Suppliers are often bound to it by their customers.
What is ISO 13485 software?
ISO 13485 software holds the requirements of the standard as a catalogue and connects them to the parts of your QMS — products, processes, owners, risks, documents, suppliers, complaints, audits and CAPA. Instead of keeping the quality manual, device files and action lists apart, you work on one set of data from which the level of fulfilment and the reports follow.
What clauses does ISO 13485 have?
Clauses 1 to 3 hold the scope, normative references and terms. The requirements are in clauses 4 to 8: quality management system, management responsibility, resource management, product realization, and measurement, analysis and improvement. Requirements in clauses 6, 7 and 8 that do not apply because of the organisation's activities or the nature of the device need not be implemented — the justification goes in the quality manual.
Does the software in the QMS have to be validated?
Yes. Clause 4.1.6 requires computer software used in the QMS to be validated for its application before first use and after changes — proportionate to the risk. Your organisation carries out the validation for its intended use; with a trial account you test Complaica against your own processes, and our consultants help with the planning.
What is the medical device file?
The file ISO 13485 asks for in clause 4.2.3 for each medical device type or family: general description and intended use, labelling and instructions for use, specifications, procedures for manufacturing, storage, handling and distribution, measuring and monitoring procedures and, where appropriate, installation and servicing requirements. In Complaica these documents hang on the product object.
How does Complaica handle complaints and CAPA?
Feedback and complaints are kept as records with owners, deadlines and status; where a report to an authority is needed, it is recorded on the case. Corrective or preventive actions follow from them, with root-cause analysis and an effectiveness check, and the reports sum everything up for the management review.
Can Complaica run ISO 13485 and ISO 9001 together?
Yes. Many requirements overlap; in Complaica both standards use the same processes, risks, actions and evidence. Documented information, internal audit and management review are kept once and used for both where the content fits — and the same goes for ISO 27001, NIS2 or the GDPR.
Is there a new edition of ISO 13485?
ISO 13485:2016 is current. ISO confirmed it in its systematic review in 2025; no new edition has been published. In Europe the harmonised version EN ISO 13485:2016 with amendment A11:2021 applies, whose Annexes ZA and ZB relate the standard to the MDR and IVDR. The new ISO 9001:2026 changes nothing in ISO 13485.
Can an existing quality manual be brought over?
Yes. Complaica imports and exports data from and to Excel and through the REST API; documents are filed on the object. Migrating your data is free of charge and supported by our specialists, so you assess the tool on your own state rather than on demo data.
Is Complaica available as SaaS or on-premises?
Both. The SaaS edition is hosted in Germany; on-premises, you run Complaica in your own infrastructure. The licence costs the same either way.
Sources References and legal sources
6 sources · ISO 13485, MDR, IVDR, FDA QMSR, … Show Hide
Legislation
Norms & standards
Only the version published in the respective official journal is legally binding. Standards are available from the publishers named.
Start ISO 13485 with Complaica
Try Complaica, ask for the price list or talk to us about your existing medical device QMS and a migration — write to us.
Thank you.
We will get back to you within one business day.
Not sent.
That did not work. Please check the fields or email us directly.